We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
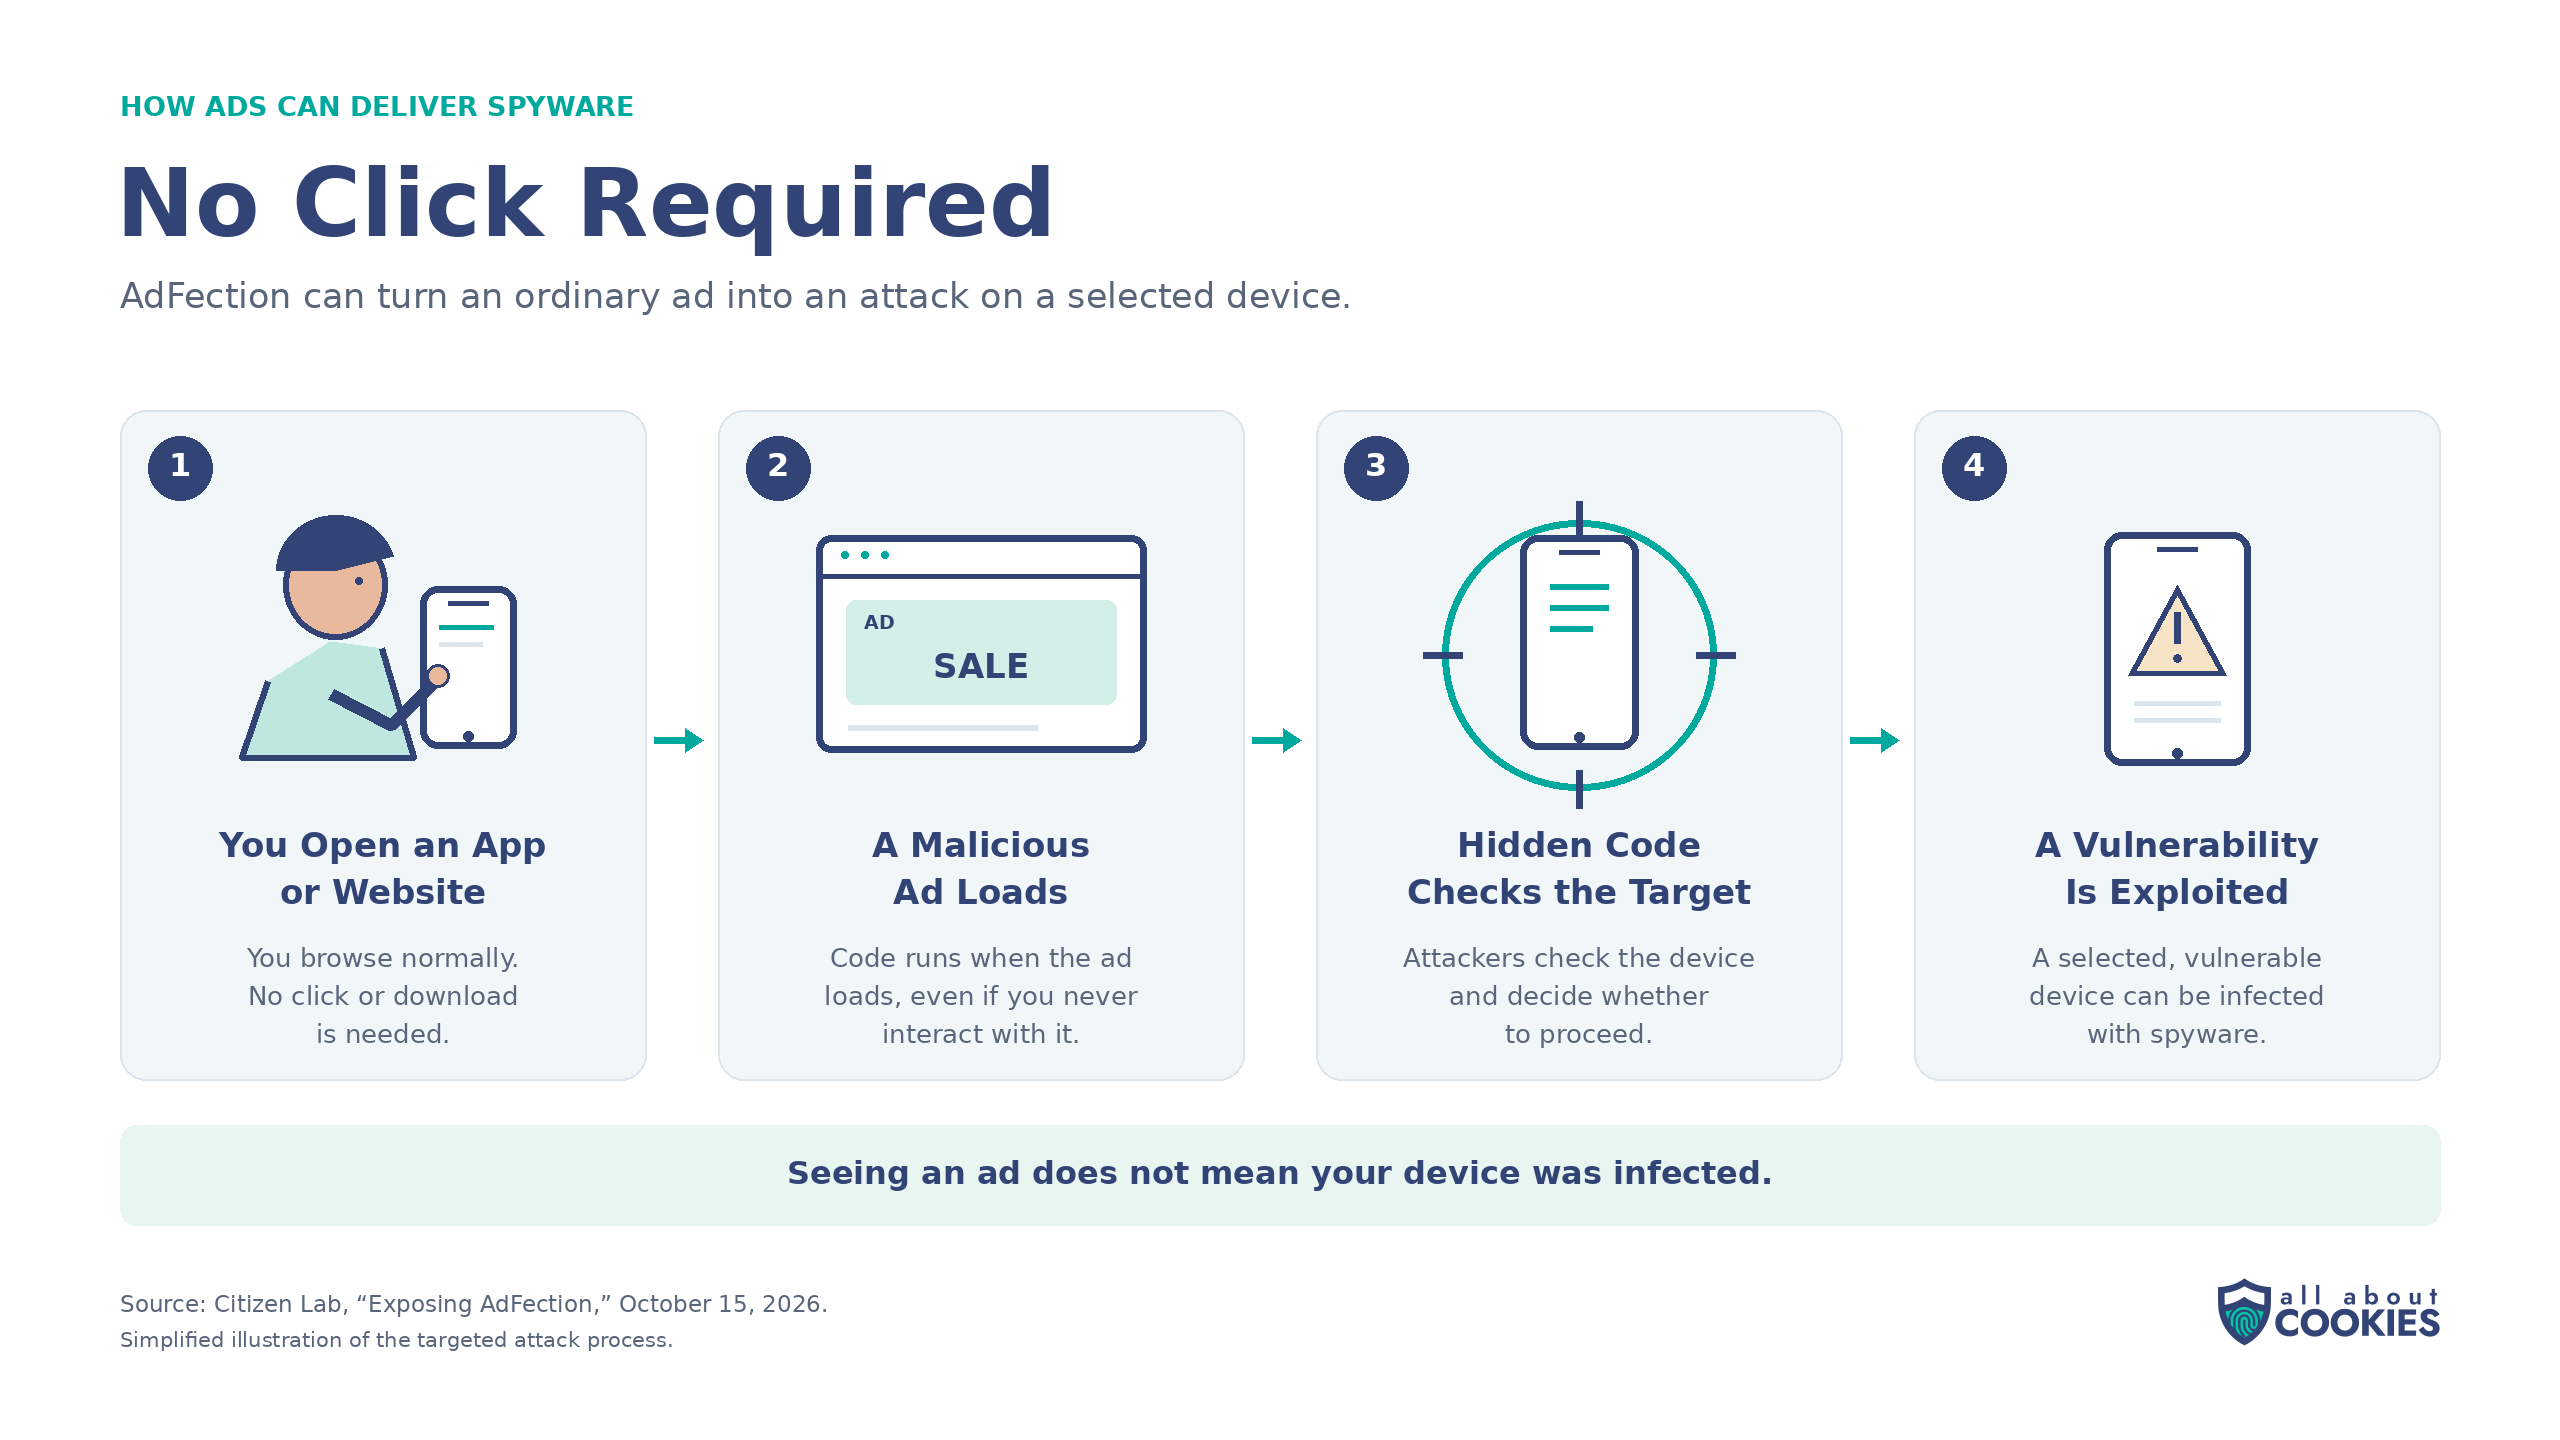
You open an app you use regularly or visit a website you browse often and see a harmless-looking ad. You don’t click the ad or download anything. But if attackers have selected your device, simply loading the ad could start a spyware attack.
Researchers at Citizen Lab uncovered a spyware delivery technique called AdFection that can infect targeted devices through online ads without requiring users to click anything.[1]
Citizen Lab describes its findings as the first public technical confirmation that mercenary spyware can be delivered through targeted online ads without any user interaction, and it has already targeted at least 45 devices at Al Jazeera.
Here's everything you should know about this spyware technique and how to protect yourself.
Join thousands who get the latest security news, scams, and policy changes every week, right to their inbox.
By submitting this form you agree to receive emails from All About Cookies and to the
privacy policy and
terms.
What is AdFection and how does it work
Every time you open an app or visit a website, an invisible auction takes place for its ad space. A bid request includes details such as your IP address, advertising identifier, or information about the app or website you're using. These bid requests are sent to advertising companies, which compete in real time for the available ad space.
Discover-Tech, an Israeli company that presents itself as a legitimate advertising business, used this system to help spyware companies target users. Citizen Lab found that Discover-Tech's real business included facilitating the delivery of mercenary spyware through online ads.
Discover-Tech operated a separate platform called Controlium, where spyware customers such as Candiru could enter identifiers, including advertising IDs and IP addresses, to select targets.
A malicious bland-looking ad, such as a generic sale banner or one impersonating a brand like Amazon or AliExpress, contains a hidden script that points to a Discover-Tech server. When the ad loads, the script sends information about your device and browsing session back to Discover-Tech.
If you're one of the selected targets, the server can return JavaScript that opens an invisible 1×1-pixel window (called an iframe) pointing to a Candiru server. This first server acts as a validator, checking whether your device matches the intended target and examining the software it runs. If the device passes these checks, the attack can proceed to exploit a vulnerability and deliver spyware.
Once infected, your device can communicate with a command-and-control server, allowing attackers to retrieve data and potentially control parts of the device remotely.
Real-time bidding (RTB) has long raised privacy concerns because it can expose information about users and their devices to numerous companies. A 2025 breach involving location data broker Gravy Analytics also showed how the advertising ecosystem can expose location information. Similarly, an Electronic Frontier Foundation report in August highlighted advertising SDKs that collect and share location data, sometimes without app developers' knowledge.
Discover-Tech also used a verification technique that made it harder for researchers to inspect its attacks. Discover-Tech included encrypted IP information in links sent to Candiru. Researchers believe this helped attackers check whether a request came from the same public IP address as the original ad impression. If a security researcher copied the link and opened it on a different device, the IP address would not match, and the exploit might not be delivered.
The extent of Discover-Tech's operations
Citizen Lab found evidence linking Discover-Tech's advertising infrastructure to attacks targeting at least 45 devices at Al Jazeera in 2024 and 2025.
Researchers also analyzed around four billion bidding records from Discover-Tech's servers covering a four-month period in 2026. These records showed that its ads appeared across nearly 200,000 unique websites and Android and iOS apps.
The ads also appeared on sensitive networks, including those associated with NATO, the United Nations, and European institutions. Researchers found evidence of Discover-Tech ads appearing on government and other sensitive networks in multiple countries.
Risks of spyware on your device
Spyware can give attackers extensive access to a compromised device:
Attackers may be able to steal passwords saved in your browser and session cookies, potentially gaining access to your email, cloud storage, and social media accounts without completing a fresh two-factor authentication check.
They may also be able to read messages and emails, access contacts and call history, or send messages to your contacts while impersonating you.
What can you do to protect yourself
Since AdFection doesn’t require a click, avoiding suspicious links alone isn't enough to protect against this type of attack. You can, however, reduce your exposure to online ads and limit the information advertising systems can collect about you.
Use an ad blocker: Install a trusted ad-blocking extension in your browser. Blocking an ad can prevent its associated script from loading. But browser extensions generally don't cover ads inside other apps. A DNS-based blocker, such as AdGuard, configured on your phone or home router, can filter some ad-related domains across apps and devices with some limitations. Some VPNs like Proton VPN NetShield also include ad-blocking and DNS filtering features.
Switch to privacy-focused browsers: Browsers such as Brave, Firefox, and DuckDuckGo offer features that block or limit trackers. These protections can reduce how much information advertising companies collect about your browsing activity.
Use a password manager: Dedicated password managers use AES-256 encryption, making it harder for hackers to access your logins and other sensitive information, such as credit card numbers, bank details, addresses, passport info, and private notes.
Limit your use of ad-heavy apps: Many apps display ads, particularly in their free versions. Consider alternatives with fewer ads or pay for an ad-free version when available.
Reset or restrict your advertising ID: Android and iPhone offer settings that let you limit how apps track you. On your iPhone, go to Settings > Privacy & Security > Tracking and turn off Allow Apps to Request to Track. On Android, you can usually find advertising ID controls under Settings > Privacy or Security & Privacy > Ads. Depending on your Android version, you may be able to delete your advertising ID.
Keep software updated: Enable automatic updates for your operating system, browser, and apps. Updates can close known vulnerabilities, although they cannot guarantee protection against unknown exploits.
The bottom line
AdFection shows that attackers may exploit online ads without requiring victims to click anything. A specially crafted ad can be enough to start an attack against a selected, vulnerable device.
Although this campaign used targeted mercenary spyware, the advertising infrastructure that delivered the ads spans a wide range of websites and apps. This raises broader concerns about how the online advertising ecosystem can be abused to track and compromise people.
Use a trusted ad blocker in your browser and consider DNS-based filtering for apps. You should also restrict access to your advertising ID where possible. But while these steps can reduce your exposure, no single measure guarantees protection against a sophisticated zero-click attack.
Get Free Parental Controls With the Dedicated Windows App
4.7
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Krishi Chowdhary specializes in digital privacy, cybersecurity, and consumer technology. He has written extensively on online privacy tools and broader cybersecurity topics, including online scams, data breaches, age verification, and emerging digital threats.
Krishi believes technology reporting should empower readers, not confuse them, and is committed to making even the most technical subjects easy to understand without compromising on accuracy or depth. His work has appeared in leading technology publications, including CNET, ExpressVPN, and TechRadar, where he has covered topics ranging from cybersecurity incidents and privacy product announcements to artificial intelligence and major technology news