Your Car Knows More About You Than You Think. Here's What Manufacturers Are Collecting [Data]
With the value of personal data at an all-time high, All About Cookies evaluated the privacy policies of major car brands to see how hard they make it to understand what information they collect about their customers.
We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
Your phone tracks you, and by now, you've probably made peace with that. But car surveillance might be the bigger threat, and hardly anyone's noticed.
That shift didn't happen overnight. As high-tech features and services have become more common in modern vehicles, auto manufacturers have been collecting more detailed customer data than ever. That trend shows no signs of stopping, as driver-facing cameras that watch for signs of distraction or drowsiness (similar to those required in new European vehicles) are making their way into more models, giving car manufacturers another potentially invasive data-collection tool.
While car companies disclose what data they collect, that information is often buried in hard-to-find privacy policies full of difficult-to-read legalese. Our team at All About Cookies evaluated the policies of 14 major automotive brands to identify how cars spy on drivers, see which data points manufacturers collect about their customers, and analyze how difficult different policies are to read and understand.
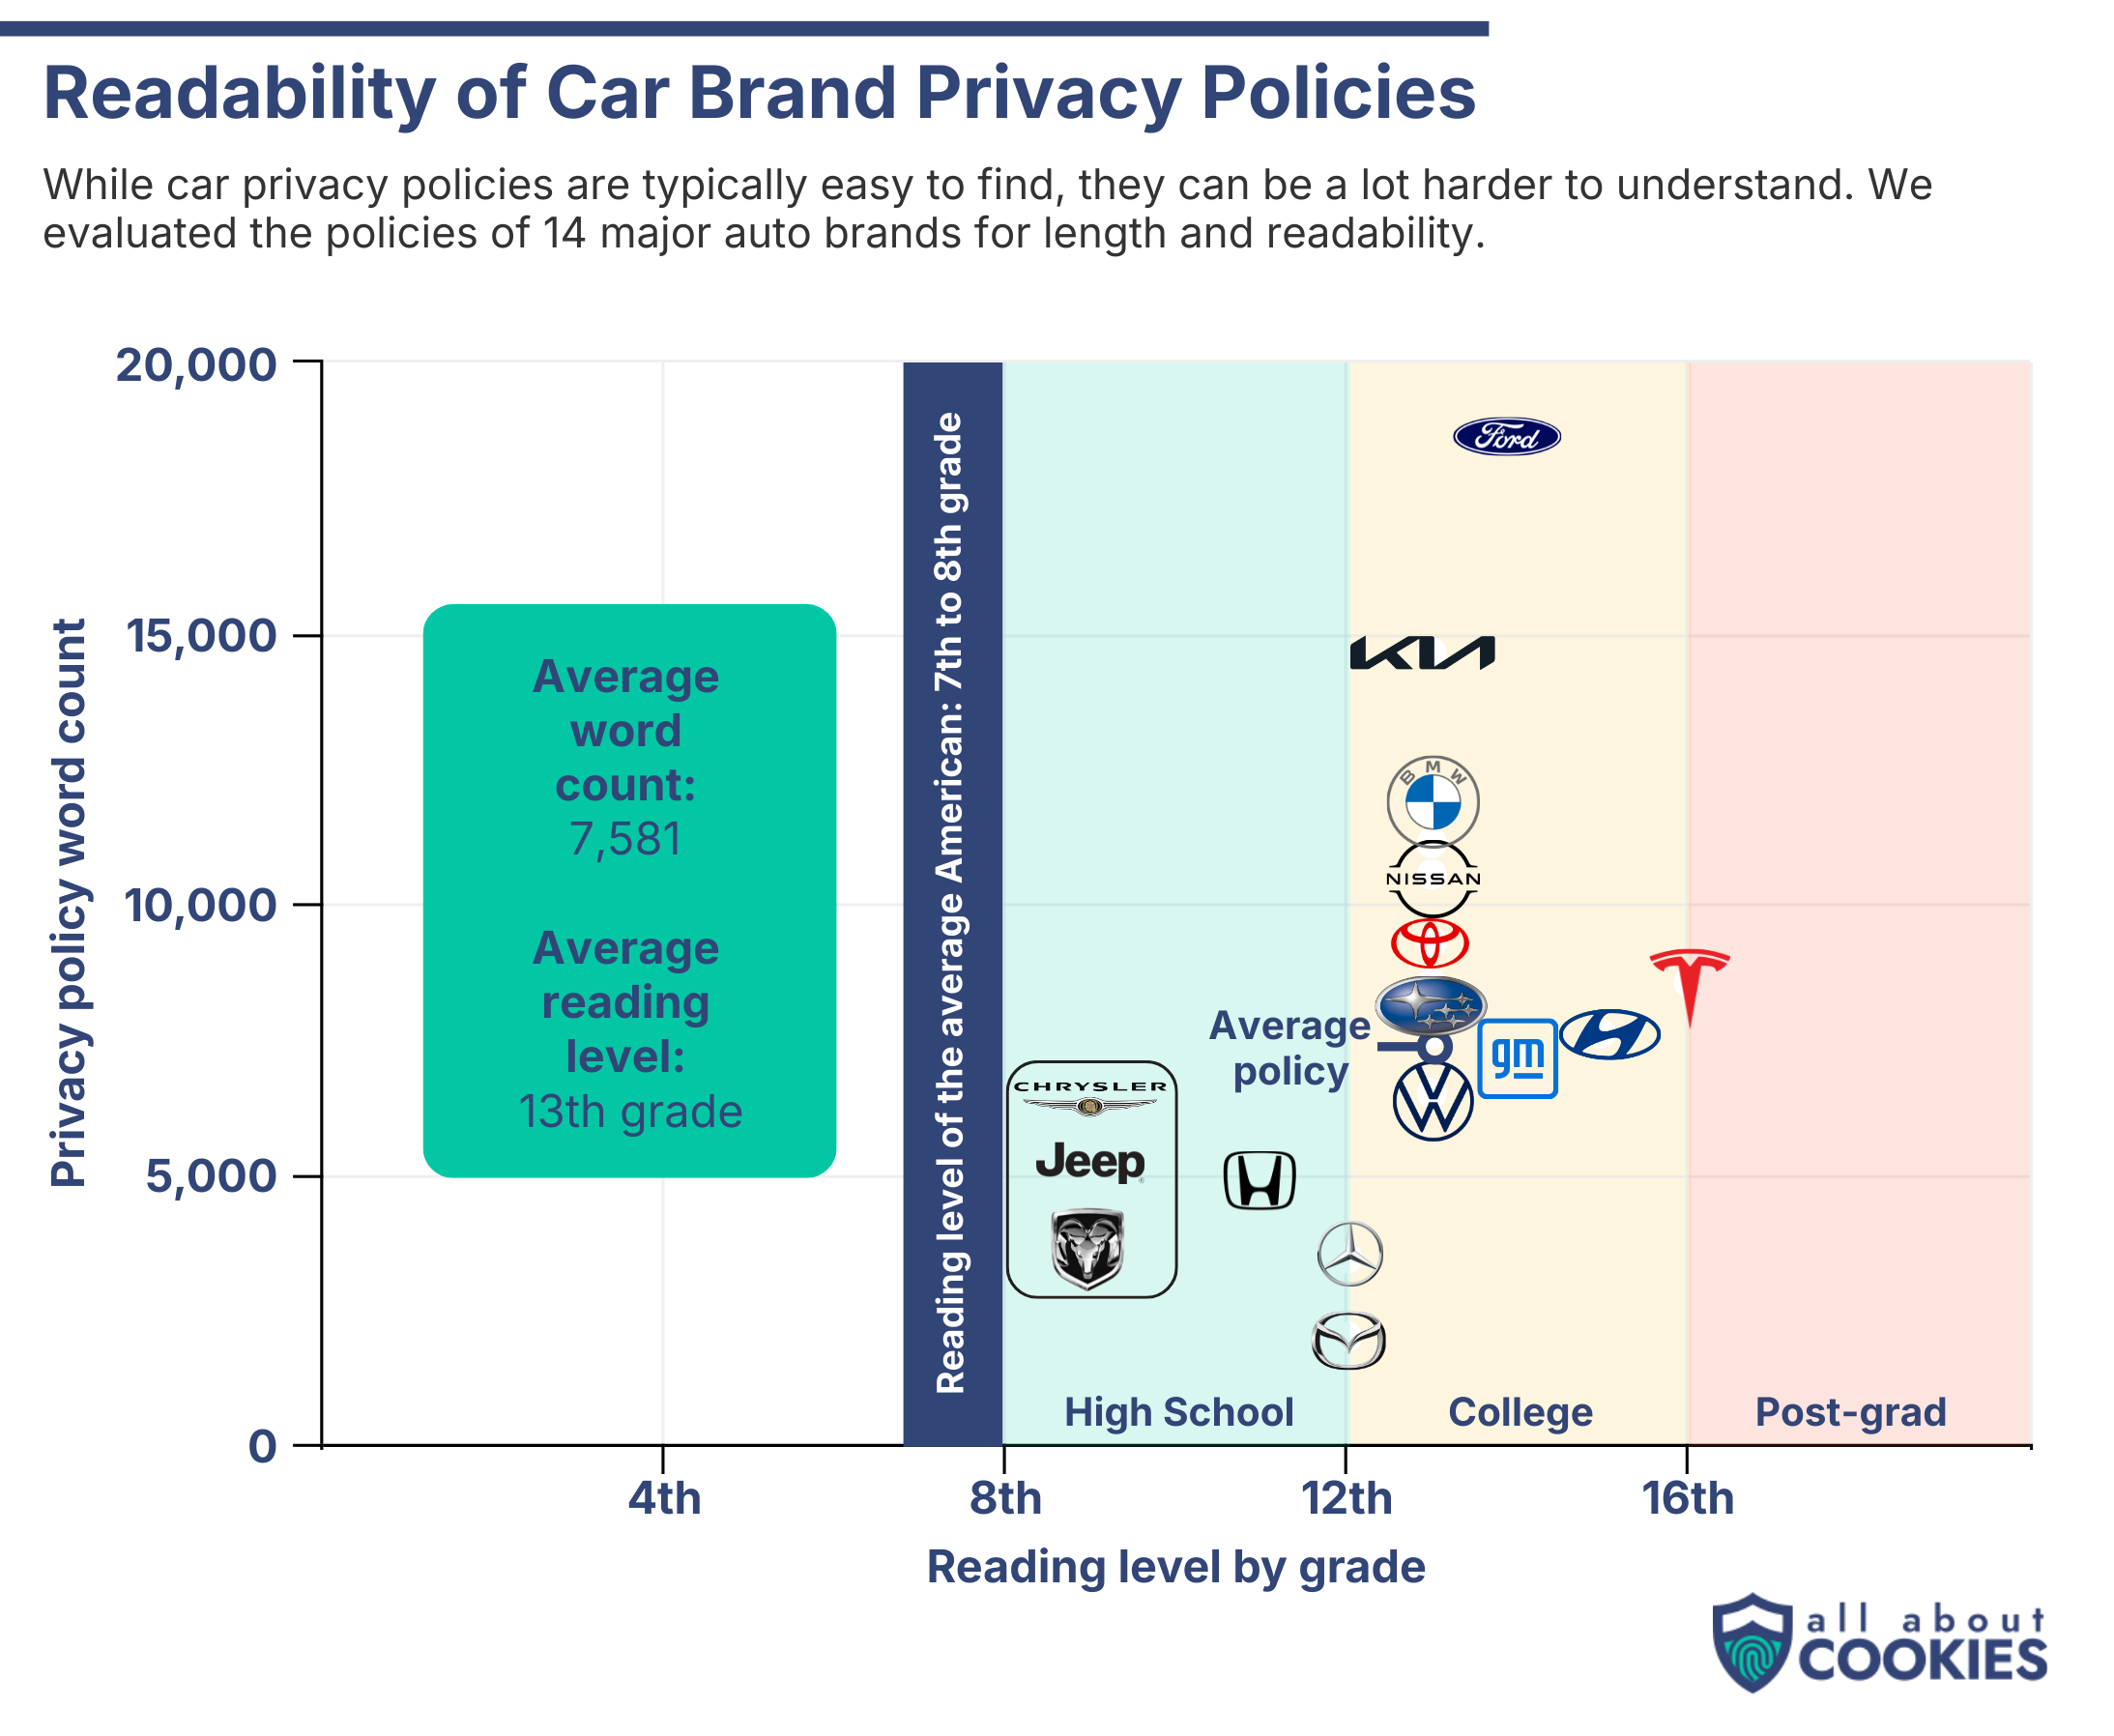
The average car privacy policy requires a 13th-grade education (college freshman level) to understand.
Despite being middle-of-the-road in terms of word count, the complexity of language in Tesla's privacy policy makes it the hardest to read of any manufacturer, requiring the same level of comprehension as topics discussed in a 400-level college textbook (16th grade).
Some of what manufacturers collect has nothing to do with driving. Nissan claims exclusive rights to the carbon credits your EV charging generates. Kia's policy lists citizenship status among the sensitive data it collects. Ford logs what you're listening to, down to the title, artist, and genre.
Ford publishes the longest single privacy document of any major brand, at 18,588 words. Kia runs longest overall, splitting more than 25,000 words across two separate policies, which is longer than The Little Prince, one of the best-selling books of all time.
How car companies collect your data
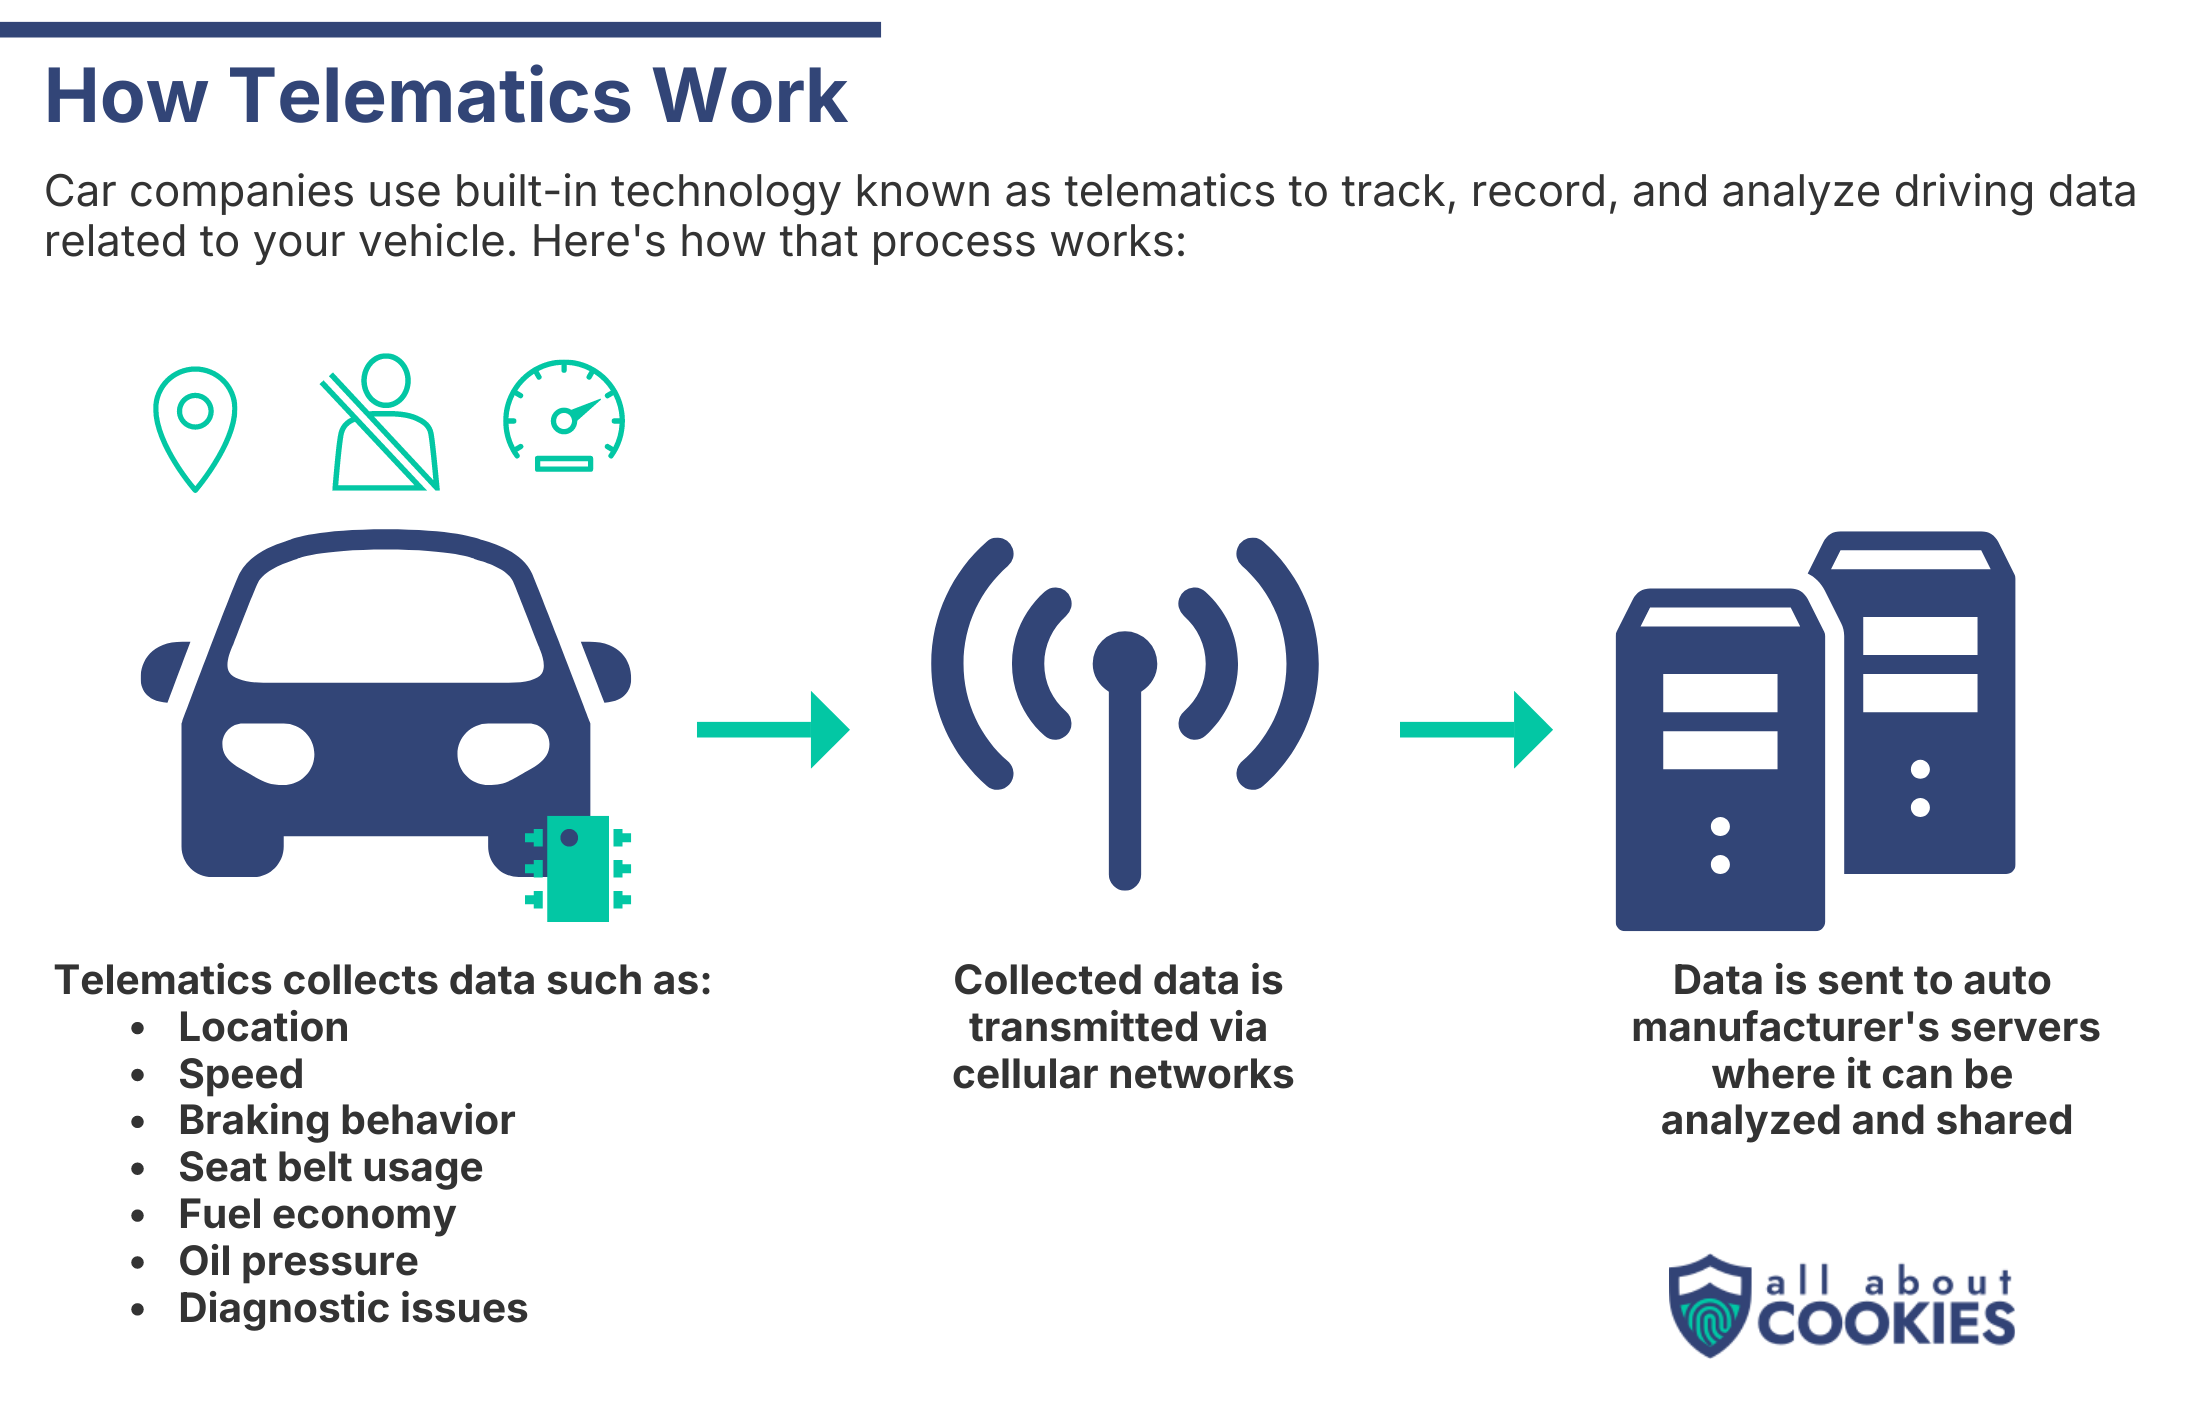
Automobile manufacturers collect personal data in several ways, with telematics built into the vehicle being one of the biggest. Telematics is a system that uses GPS and other onboard diagnostic technology to record, analyze, and report data such as a vehicle’s movement, location, speed, mechanical health, and more. In an increasing number of new vehicles, telematics also includes driver-facing cameras meant to track distraction or drowsiness behind the wheel.
The telematics system records collected data on a small telematics device, also known as a black box. This box has a SIM card and modem that lets it transmit recorded data via cellular networks. The data is then sent to dedicated servers, where auto manufacturers can access and share it.
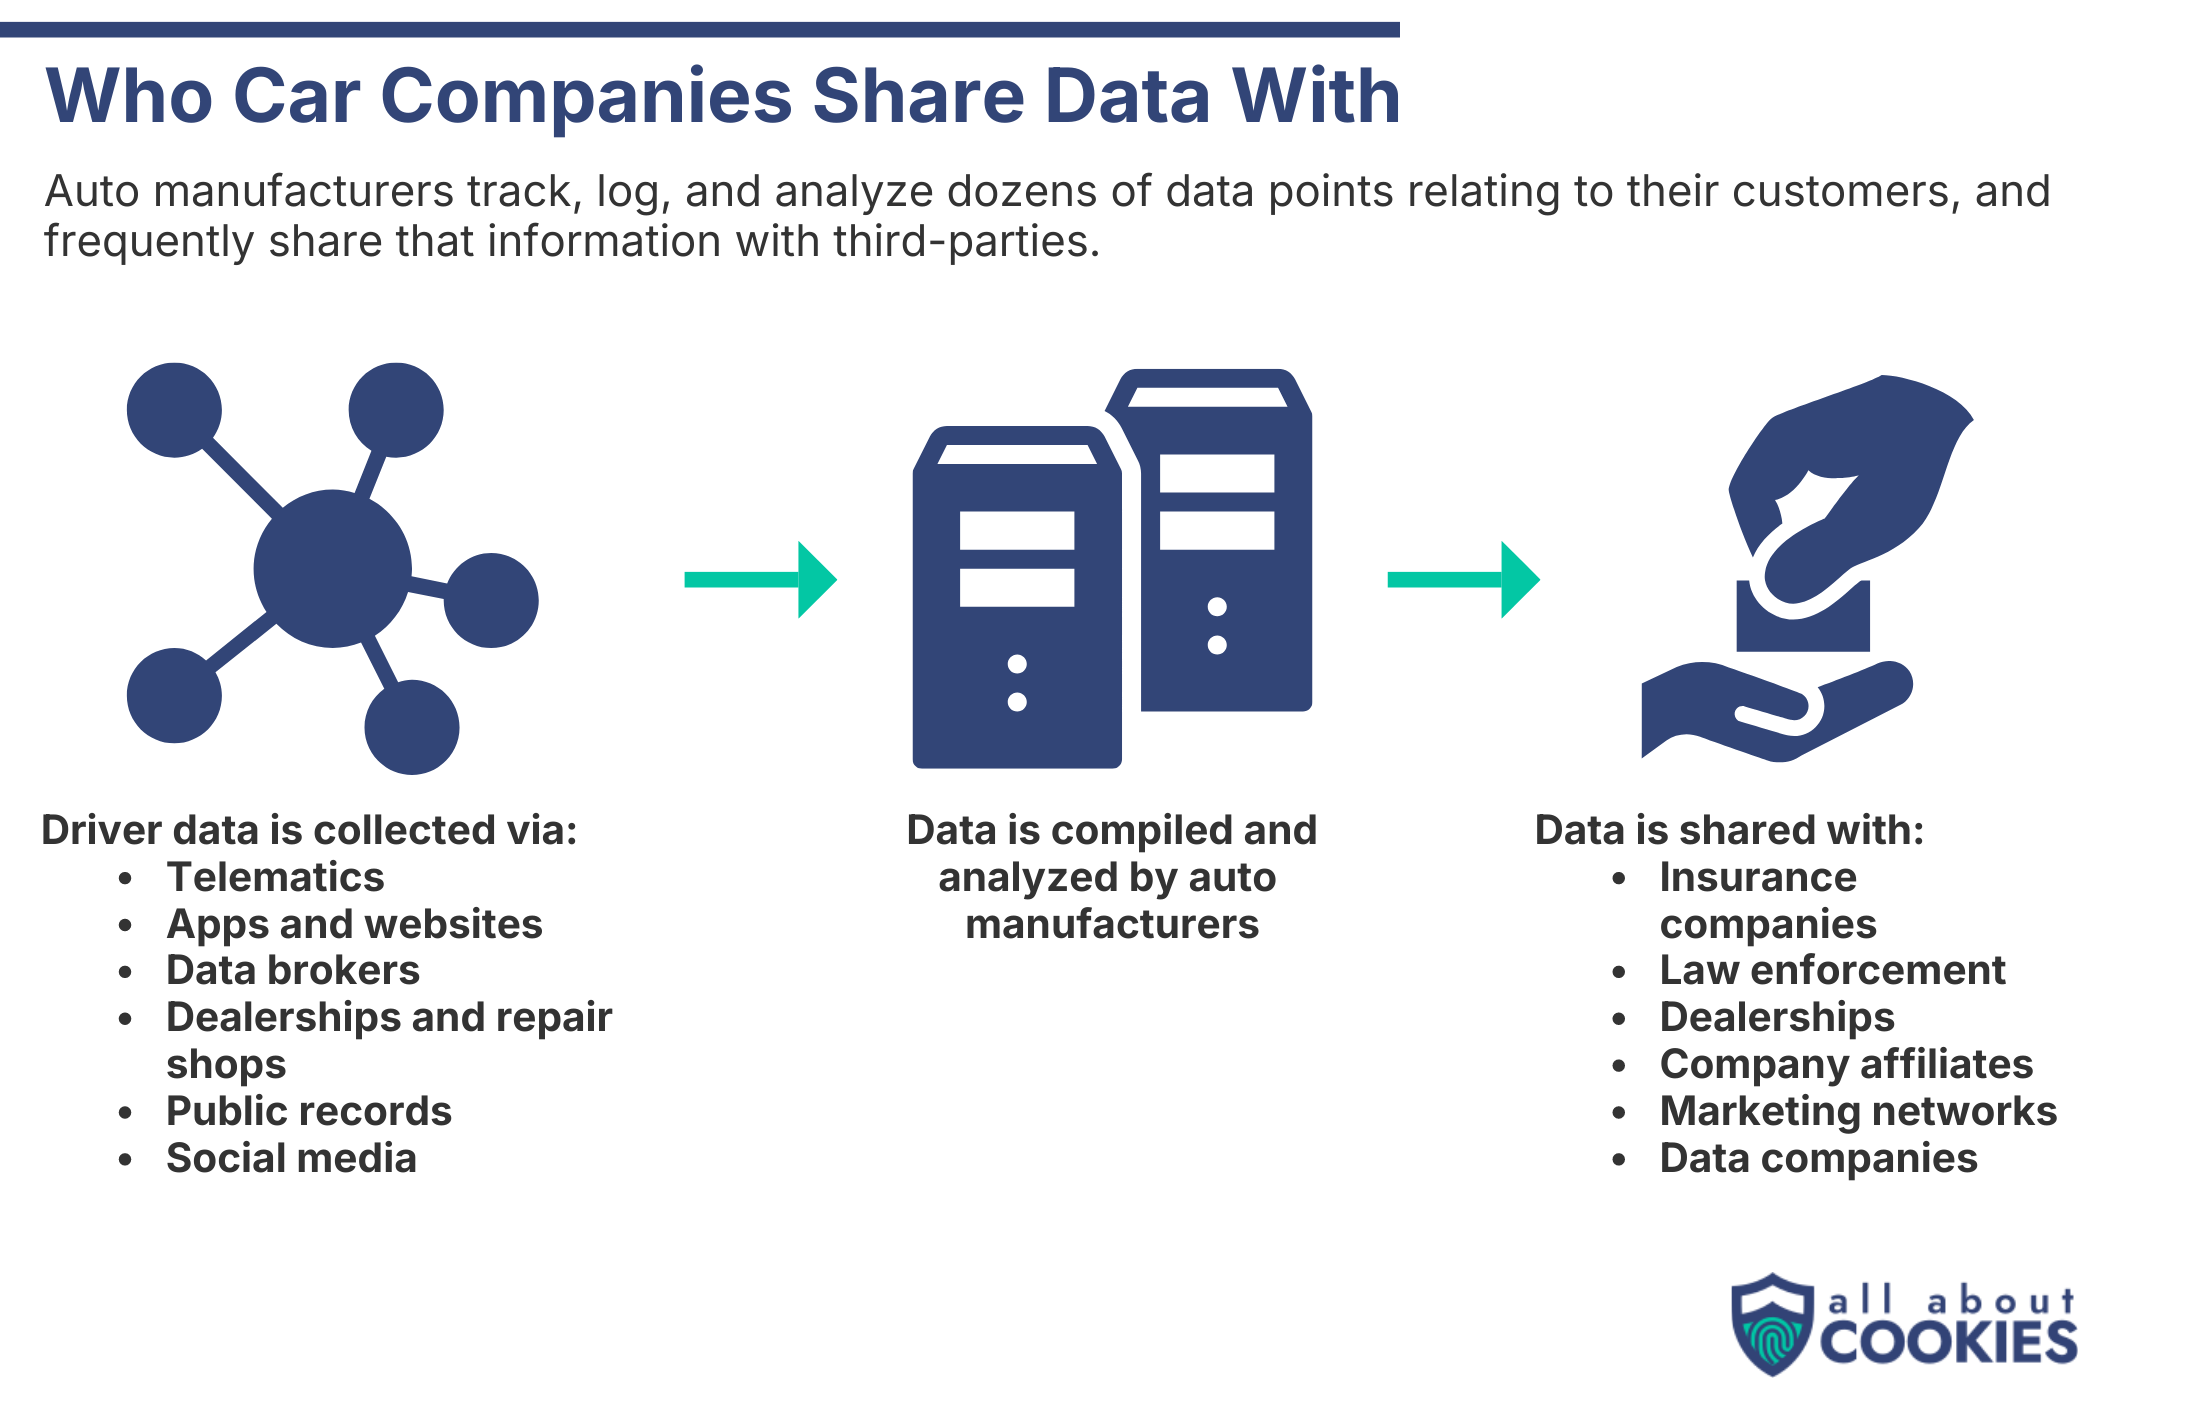
Car companies also pull personal data from far more than the vehicle itself. Websites and apps drivers use are tracked via cookies and browser fingerprinting; dealerships pass along sales and service records; and many manufacturers buy additional data from brokers, marketing partners, and public or social media sources. Some also record customer service calls and in-vehicle voice assistant conversations. None of this requires the car to be in use, as it happens through account sign-ups, app permissions, dealership paperwork, and outside data purchases.
Who car companies share driver data with
Data collected by auto manufacturers doesn’t stay in-house. While car companies send driver data to other branches of their parent company, such as dealerships and financing and insurance departments, they also send data to third-party companies and services. These typically include insurance companies, advertising and marketing networks, law enforcement, and data and analytics companies.
This kind of data sharing isn’t necessarily good for drivers. In January 2025, the Federal Trade Commission took action against General Motors and its OnStar brand for using misleading tactics to get consumers to sign up for OnStar and then selling driving behavior data collected through that program to third-party consumer reporting agencies without customer consent. That data was then used by insurance companies to increase driver premiums, in some cases significantly.
In January 2026, the FTC banned GM and OnStar from sharing this kind of data with outside consumer reporting agencies for five years, and has required them to get explicit permission to collect and share driver data for the next 20 years. Additionally, the company has faced several lawsuits that could cost it millions in damages.
Sharing with outside parties isn't limited to insurers. In its Privacy Not Included review of 25 car brands, the Mozilla Foundation found that more than half of the car brands studied (56%) will hand over driver data to law enforcement or government agencies on an informal request, without requiring a warrant or subpoena. That same review also named cars the “worst product category for privacy” they had ever reviewed.
Car companies with the hardest-to-read privacy policies
Many customers may not realize their car is collecting all this information because while auto manufacturers are required to report on the data they gather, they do so in privacy policies that are often difficult to read and understand.
We ran 18 privacy documents from 14 major car companies through a readability app, which scored each one based on the level of education needed to comprehend it, using factors like word count and complexity. Four brands publish a separate policy covering in-vehicle and connected services data, so we scored those separately.
Tesla's privacy policy is the hardest to understand of any major brand, requiring the reading level of a college senior (grade 16), making it equivalent to the kinds of content that may be taught in a 400-level college course. Hyundai follows closely, requiring a 15th-grade education. Ford and General Motors are tied for the next-hardest, each requiring a 14th-grade (college sophomore) reading level. Given that the average American reads at a 7th- or 8th-grade level, these policies are written well beyond the comprehension of many customers.
In fact, every single automaker’s privacy policy is beyond the average person’s reading level, as Stellantis's combined Chrysler/Jeep/Dodge/Ram privacy policy is the easiest to read of any major automaker this year, and that still requires a 9th-grade reading level. Honda (grade 11) and Mercedes-Benz and Mazda (both grade 12) round out the easiest-to-read group.
Ford's consolidated privacy notice is the longest single document reviewed this year, at 18,588 words, followed by Kia's general privacy policy at 14,631 words. Kia is the wordiest brand overall, since its separate Kia Connect policy adds another 10,942 words for a combined 25,573.
The average brand's primary privacy policy now runs 8,422 words and takes about 42 minutes to read, up 12% from the 7,505-word average we found in 2024.
Company
# of words in policy
Reading level (grade)
Notable policy elements
BMW
11,111
13
Pulls calendar events, contacts, and notifications off the vehicle. Collects 3-D surround images around the car, and data from physical vehicle inspections at end of lease.
Chrysler/Jeep/Dodge/Ram
5,157
9
Other drivers granted Connected Services access may see the account holder's personal data.
Ford
18,588
14
Tracks what's playing in the car, including radio presets, volume, and the specific titles, artists, and genres you listen to. Lists a no-LLM-training promise that applies only to Connecticut residents.
General Motors
7,213
14
Super Cruise logs when it decides a driver is distracted or drowsy.
Collects student ID information, number and ages of children, and languages spoken.
Hyundai
7,588
15
Uses vehicle location "regardless of location data settings" to support repossession by Hyundai Capital America in delinquency cases.
Kia
14,631
13
Collects genetic information and citizenship status. Also uses browser fingerprinting and cross-device recognition.
Kia Connect
10,942
15
Includes a feature called "My Car Zone" which lets the car owner monitor another driver using the vehicle, and recommends but does not require consent to do so.
Mazda
1,987
12
Infers household income from collected data. Sends data to listed preferred dealerships by default unless turned off.
Mazda Connected Privacy Policy
2,864
14
Driving data (acceleration, speed, steering, braking) is transmitted at every ignition-off, per trip. States that data collection does not end after selling the car or ending a lease.
Mercedes-Benz
3,431
12
Policy states driver data may be used to train, test, and refine AI models and algorithms.
Nissan
10,534
13
Claims exclusive rights to the carbon credits generated by your EV's charging data. Collects religious affiliation and national origin.
Subaru
8,512
13
Collects your social media profile photo and tracks engagement with Subaru's social pages.
Subaru Vehicle Privacy Notice
4,266
13
EyeSight stores stills of people and objects outside the vehicle. Independent repair shops can pull on-board data with their own tools outside of Subaru's control.
Tesla
8,537
16
Collects "a mathematical representation of your face" as Government ID Data for automated identity verification during purchase, financing, and delivery.
Toyota
9,271
13
Has a dedicated "AI Research" data category, allowing it to use customer data to train and fine-tune AI models.
Toyota Vehicle Data Transmission
482
12
Reports non-precise location, driving, and health data as being used for internal research.
Volkswagen
6,477
13
DriveView shares driving behavior and GPS with named insurance companies for up to 20 days or 20 trips.
Average
7,581
13
-
How vehicle policies may get more complicated in the near future
Whenever new technology becomes commonplace in the automotive industry, it needs to be added to relevant privacy policies, and that additional copy may make those policies harder to read. One specific kind of new technology with major privacy implications is already making its way into more and more vehicles: driver-facing cameras.
Under the European Union's General Safety Regulation, Advanced Driver Distraction Warning (ADDW) systems became mandatory for new vehicle types in July 2024 and for all new vehicles sold in the EU as of July 7, 2026. The regulation doesn't name a specific technology, but detecting visual distraction reliably takes a direct read on the driver, so nearly every automaker complies with an infrared driver-facing camera tracking eye gaze and head position.
The introduction of this law has led many to wonder whether a similar requirement may be coming to the United States. While nothing has officially been put into place at present, there are signs that point to the potential for such a system to be implemented in America.
The HALT Drunk Driving Act,enacted in 2021 as part of the Infrastructure Investment and Jobs Act, directed the National Highway Traffic Safety Administration (NHTSA) to create a federal safety standard by 2024 requiring technology that passively monitors drivers for impairment and prevents or limits operation of the vehicle if it detects it.
NHTSA missed that deadline and is now nearly two years past it, though the law allows a three-year extension that pushes the final deadline to November 15, 2027. The agency published an advance notice of proposed rulemaking in January 2024 and collected more than 3,000 comments, but has never issued a proposed rule.
In a February 2026 report to Congress, NHTSA said no commercially available system meets the law's requirements, warning that "even a 99.9 percent detection accuracy level could result in millions to tens of millions of instances each year where the technology would incorrectly prevent or limit drivers from operating their vehicles, or fail to prevent or limit impaired drivers from doing so.”
Driver-facing cameras are one potential form of technology that could be used to comply with this act.
Even without a federal mandate, several automakers already have driver-facing cameras that track eye and head position for signs of distraction, including Ford BlueCruise, GM Super Cruise, and Tesla's Full Self-Driving, with more and more manufacturers and models including these kinds of systems as time goes on.
Tips for keeping your personal data safe on and off the road
Your car collects more about you than most people realize, and most of it leaves your vehicle without any action on your part. Here's what you can do to better protect your privacy on the road:
Take control of what you share with websites and apps. Your car isn't the only place your data is being collected. Knowing how to change your privacy settings across your devices and accounts is one of the most effective steps you can take to limit your exposure.
Protect your identity if your data ends up in the wrong hands. Connected car data has already reached insurers and consumer reporting agencies without drivers' knowledge, and a leak or breach puts far more than your commute at risk. Using one of the best identity theft protection services adds monitoring and recovery support if your personal information gets compromised.
Get your personal details out of data broker databases. Your car's data is only valuable to advertisers and brokers when it can be tied to the rest of your profile: your name, address, phone number, and household details. Using one of the best data removal services sends removal requests to the people-search sites and marketing brokers holding that information, shrinking the profile your driving data can be matched against.
How common is an intentionally complex/long privacy policy?
Privacy policies are undoubtedly commonly long and complex and often contain vague or ambiguous language, which on one hand, creates flexibility and minimizes risks for the entity who has the policy. However, it makes it difficult for consumers to comprehend and rely on to develop an understanding of what happens with their information.
How can people be more aware of what is being collected from them?
As lengthy as privacy policies generally are, consumers should review them upfront to understand what information is being collected, how it will be used, and who it will be shared with.
Users should not automatically click “yes” when asked to consent to the use of their information but rather consider whether the convenience and other benefits of whatever service is being offered outweigh the loss of their privacy.
How can consumers take their privacy into their own hands and stay safe while being able to enjoy the convenience of smart vehicles?
Drivers should consult their car’s privacy policy to understand what information the car will seek to collect, use, and share, and whether and how they can opt out of providing certain information. Privacy-conscious users should refrain from downloading their car’s app, which may collect data even when a user is not in the car, and refrain from enabling Apple’s Car Play or Android Auto Play.
Privacy-conscious users who pair their devices with their car through Bluetooth should decline consent if asked to share their address book or other information. All drivers should delete their data when they turn in a car at the end of a lease or rental. Users should also be sure to delete any apps and terminate their accounts at the end of a lease.
Are there strategies companies use to have consumers consent to more surveillance/data collection when crafting privacy policies?
Some car companies put in their privacy policies that by merely operating a car and/or using associated services, the user is deemed to have consented to the collection of their personal information.
Answers have been edited for clarity and brevity.
Methodology
The official privacy policies for each of the 14 automakers were copied and pasted into the Hemingway Editor App, which evaluated them for reading level, sentence count, and length. All readability figures and word counts cited in this piece come from that Hemingway-based scoring. Reading time was determined by copying and pasting each policy into the Paraphrasing.io readability checker. The most recent versions of each manufacturer’s policies (as of July 2026) were used.
4.8
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Steph Trejos is a Certified Anti-Money Laundering Specialist (CAMS), a credential that reflects deep expertise in financial crime, fraud patterns, and cyber threats. As a Senior Product Testing Editor at All About Cookies, she has personally evaluated nearly 200 digital security products and brings that forensic rigor to every review she oversees. Before joining AAC, she produced publications on financial crime and cyber threats at ACAMS.
Josh Koebert is a seasoned data journalist whose work has appeared in top-tier outlets including CNET, PCMag, Forbes, TechCrunch, and a range of other respected media platforms. His work explores topics relating to privacy, data security, and technology in an increasingly digital world.