We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
An interview invitation from Meta could be welcome news after weeks of job hunting. Scammers are counting on you being excited enough to follow their instructions.
Malwarebytes researchers uncovered fake interview-booking websites impersonating Calendly and Meta Careers.[1] They ask visitors to schedule a call before requesting their Facebook and Google passwords, along with the security checks needed to get into those accounts. The company published its findings on October 14.
Join thousands who get the latest security news, scams, and policy changes every week, right to their inbox.
By submitting this form you agree to receive emails from All About Cookies and to the
privacy policy and
terms.
How the fake interview works
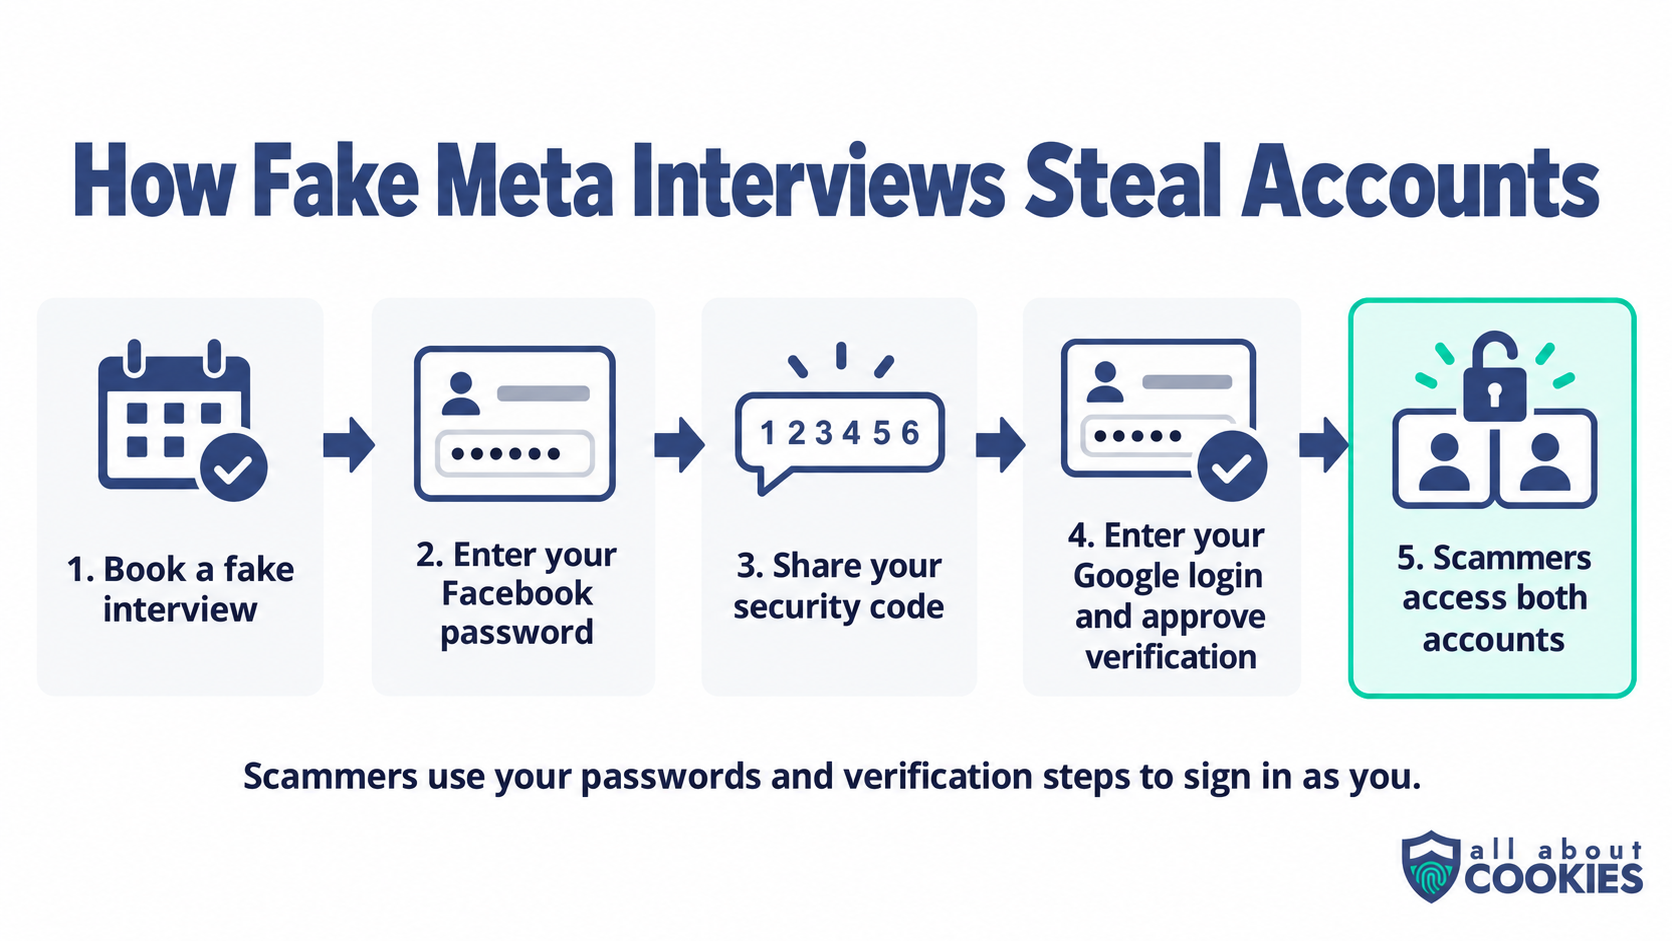
Visitors pick a time, provide contact details, and complete a fake CAPTCHA. Then the page asks them to log in to Facebook. The imitation login window includes a fake address bar showing a Facebook URL. It also asks for a two-factor authentication code.
Next, it asks them to sign in to the Gmail address associated with the Facebook account. Fake Google screens collect passwords and can instruct visitors to enter verification codes or approve a sign-in prompt.
Meanwhile, attackers try those credentials on the real services, using the victim’s responses to complete the login. The pages have no affiliation with Meta, Calendly, or Google.
Why two-factor authentication isn’t enough here
Two-factor authentication helps protect your account if someone steals your password. But entering a security code on a phishing page can give the attacker the next thing they need to sign in.
A genuine code can arrive because someone else is trying to access your account. Receiving it doesn’t mean the page asking for it is legitimate.
Google supports passkeys, which let you sign in using your device’s fingerprint reader, face unlock, or screen-lock PIN. They’re tied to the genuine service, so you can’t accidentally type one into an imitation login form. Only create them on devices you own and control.
Check the browser’s actual address bar before entering login details. A Facebook address drawn inside a webpage doesn’t establish where you are signing in.
What to do if you shared your login
Go directly to the affected service through its official app or website and change your password. Change it anywhere else you reused it, too.
For Google, review recent security activity and connected devices, then remove unfamiliar access. Check that your recovery email address, phone number, and authentication methods still belong to you.
In Gmail, look for forwarding rules or filters you didn’t create. Those settings could let someone receive copies of your messages or hide security alerts.
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Thomas Kent is a multi-disciplined reporter with over a decade of experience covering online platforms, digital trends, and consumer-facing tech.
Tom focuses on digital privacy, data tracking, and user behavior, with a particular interest in how cookies, online surveillance, and platform design shape the modern internet experience. His reporting takes a research-driven, news-focused approach, translating complex technical topics into clear, accessible insights.