Trump Mobile Leaked Customer Data Again. Here's What Hackers Know About You
A ransomware group has published the data of 3,615 Trump Mobile customers online, putting their phone numbers and other personal details at risk of scams and identity theft.
We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
After exposing the personal information of around 27,000 people in May this year[1], Trump Mobile, the network associated with the Trump family, has suffered yet another data breach affecting at least 3,615 customers, this time reportedly as a result of a cyberattack.[2]
If you’re a Trump Mobile customer or have paid a deposit in the past, your details may now be circulating on the dark web, where they could be sold or used by cybercriminals. The exposed information includes names, email addresses, phone numbers, home addresses, and order details.
These details could be used to target you with phishing scams, SIM-swapping attacks, and financial fraud, and bad actors could also combine them with information from previous breaches to build a more complete profile of you.
Here’s everything you should know about the data breach and the steps you can take to protect yourself.
Join thousands who get the latest security news, scams, and policy changes every week, right to their inbox.
By submitting this form you agree to receive emails from All About Cookies and to the
privacy policy and
terms.
What information did the hackers steal
According to reports from Straight Arrow, Trump Mobile was infiltrated by a newly formed ransomware group called BYOD, which published the stolen data on a dark web leak site last week alongside a message about the alleged breach.
BYOD claims it contacted Trump Mobile to inform the company about the breach, but says it was told, “We have no team to handle this.” The message claimed that the group had data belonging to at least 3,615 customers, including their personally identifiable information and telecom details. It also encouraged dark web buyers to view the leaked dataset.
Straight Arrow reviewed the data and found the following information:
First and last names
Email addresses
Phone numbers
Home addresses
Order details, including the $100 deposits for T1 phones and purchases of mobile plans
Other telecom details, as claimed by the attackers
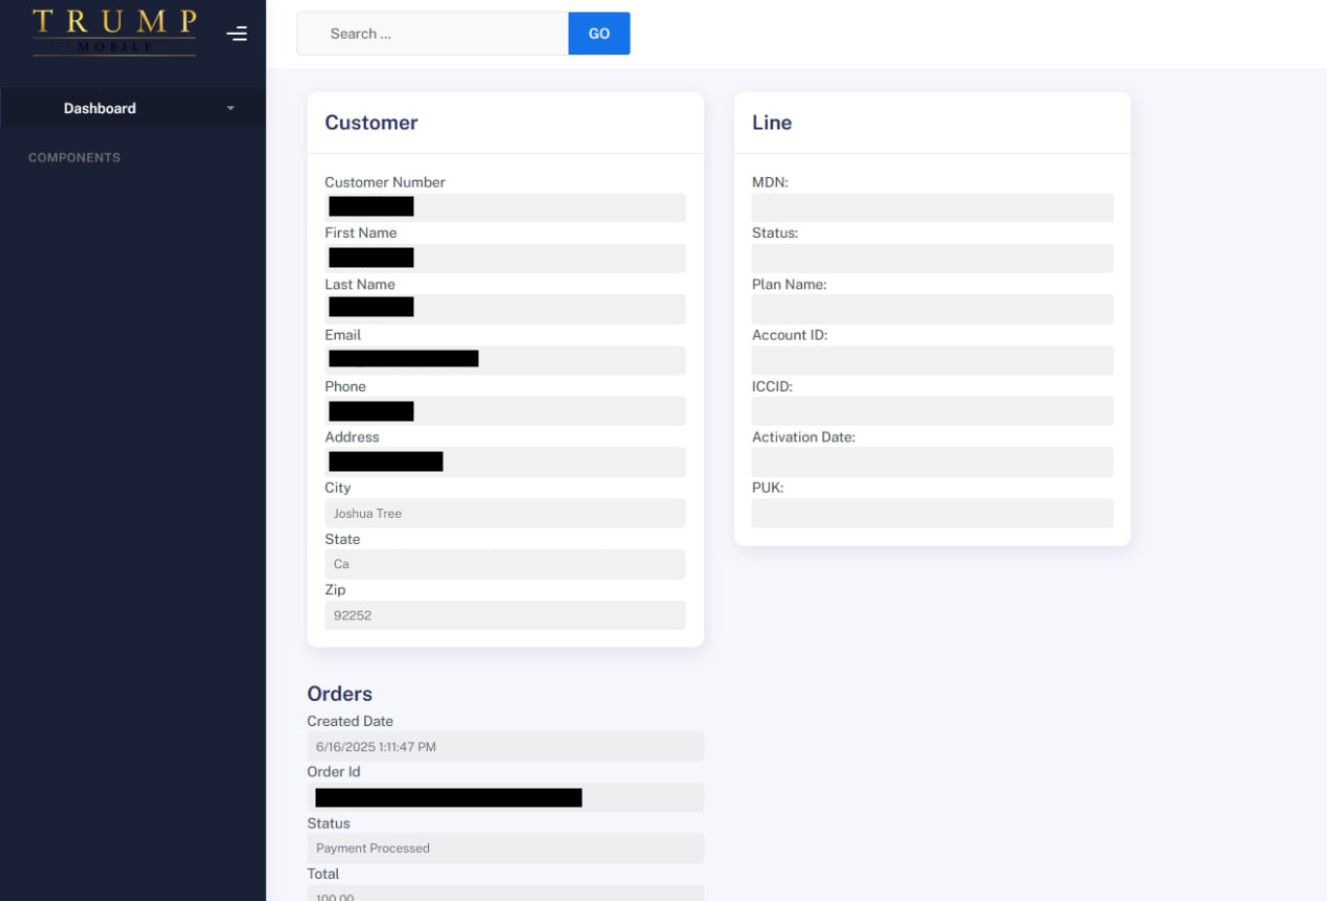
BYOD also claims that it still has access to Trump Mobile’s backend dashboard and provided Straight Arrow with a screenshot showing a customer’s personal details.
Straight Arrow
A BYOD representative told Straight Arrow that the group gained access by infecting an employee of Liberty Mobile, a Florida-based company, with malware. Trump Mobile is owned by T1 Mobile, which licenses the brand from The Trump Organization. The exact details of the attack and the tools used have not been independently verified.
No member of the Trump family appears to be among the affected customers, according to Straight Arrow’s review. However, the leaked data includes personal information belonging to Eric Brunnett, the Trump Organization’s vice president and chief information officer.
This is not the first time Trump Mobile has been found to be exposing people’s information. As per a Guardian report in May 2026, a security flaw on Trump Mobile’s website exposed the personal details of around 27,000 people who had filled out pre-order forms for the T1 phone. This included names, mailing addresses, phone numbers, email addresses, and order identifiers.
Trump Mobile launched in June 2025 at $499, with a $100 deposit, and was initially due to ship in August 2025. However, customers only started receiving their deliveries after an 11-month delay.
Why a telecom data leak can be dangerous
A data breach of this scale can create several privacy and security risks, especially because telecom information can be combined with other personal data to make scams more convincing.
SIM swapping: Probably the biggest risk of a telecom data breach is SIM swapping, where malicious third parties use information about you to convince a carrier to move your number to a SIM card they control. Once they take control of your number, they can receive your calls and texts, including one-time codes for sensitive accounts such as banking, email, or cryptocurrency accounts.
Phishing: Malicious parties may impersonate Trump Mobile and send messages claiming that your account needs “verification” or that you need to change your password. These messages often contain links that could install malware or spyware on your device or take you to a fake website designed to steal your credentials. The leaked information can make these messages more personal and, therefore, more convincing.
Vishing: Similarly, scammers may attempt voice phishing, or vishing, scams while pretending to be Trump Mobile support. They could use information from the breach to gain your trust before asking for your credit card details, passwords, or verification codes.
Identity theft: When combined with data from earlier breaches, such as your date of birth or Social Security number, criminals could use the stolen information to build a much more complete profile of you. They could then use that information to pass identity checks or open new lines of credit in your name.
What can you do to protect yourself
If you’re a Trump Mobile user or have paid a deposit in the past, here are some steps you can take to stay protected amid this data breach.
Treat any Trump Mobile contact as suspicious: It's unclear if the company has notified its customers about the breach, so if you have paid a deposit or bought a plan, it’s worth assuming that you could be affected. Be wary of any texts or calls claiming to be from Trump Mobile, and don’t click on links in messages from unknown senders.
Lock down your number and your logins: Ask your carrier to add an account PIN and port-out lock to help prevent SIM-swapping attacks. If you use SMS-based two-factor authentication (2FA), consider moving your accounts to an authenticator app or passkey instead.
Use a third-party antivirus program: Many reliable third-party antivirus solutions come with real-time web protection that can flag suspicious links before you interact with them. This can help protect you from malicious websites and phishing links, even if you accidentally click one.
Use an identity theft protection service: These tools look for your leaked data on the dark web and known breached databases, helping you spot potential misuse of your personal information. Many services also offer professional restoration specialists who can help you regain control of your identity after a data breach.
The bottom line
After lengthy delivery delays and controversies surrounding its phones, Trump Mobile has now been hit by another cybersecurity problem, which has resulted in sensitive personal data belonging to thousands of customers ending up on the dark web. These details could be used to target victims with convincing phishing scams, financial fraud, or even identity theft.
Trump Mobile has not publicly confirmed notifying customers about the breach, and reportedly told BYOD it doesn't have a team to handle the situation. This makes it particularly important to stay vigilant and follow good cybersecurity hygiene, including being wary of suspicious calls and messages, locking down your phone number with a carrier PIN and port-out lock, and using real-time web protection to block malicious links.
4.8
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Krishi Chowdhary specializes in digital privacy, cybersecurity, and consumer technology. He has written extensively on online privacy tools and broader cybersecurity topics, including online scams, data breaches, age verification, and emerging digital threats.
Krishi believes technology reporting should empower readers, not confuse them, and is committed to making even the most technical subjects easy to understand without compromising on accuracy or depth. His work has appeared in leading technology publications, including CNET, ExpressVPN, and TechRadar, where he has covered topics ranging from cybersecurity incidents and privacy product announcements to artificial intelligence and major technology news