This Google Ad Could Lock up Your Browser With a Fake Virus Warning. Don’t Call the Number
Researchers have found a malicious Google ad that can hijack your browser with fake virus warnings and pressure you into calling a scammer posing as tech support.
We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
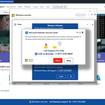
Netskope researchers have discovered a new scam that uses a fake virus warning to scare victims into calling a supposed tech support number.[1] All the victim has to do is click on an innocent-looking ad on a legitimate website, and suddenly their screen goes blank, alarms start blaring from their speakers, their mouse cursor vanishes, and Microsoft says that their computer is infected.
Panic-stricken, they press Escape, but nothing happens, and a phone number flashes on the screen: “Call immediately.” If they call that number, there’s a scammer waiting to extract personal information such as their name, address, phone number, and even credit card numbers. Giving away such sensitive information may lead to phishing scams, financial fraud, and even identity theft.
The scam reached at least 619 organizations over a two-week window, with 62% of affected organizations in the United States. Here’s everything you should know about this new attack and the steps you can take to stay safe.
Join thousands who get the latest security news, scams, and policy changes every week, right to their inbox.
By submitting this form you agree to receive emails from All About Cookies and to the
privacy policy and
terms.
How does this Google Ads scam work
As per Netskope’s report, the attack starts while you’re browsing a legitimate website, such as a sports site or a weather site, and you see a Google ad pop up. The scammers have paid for Google Ads so that their ads are shown to users just like any other ad would be.
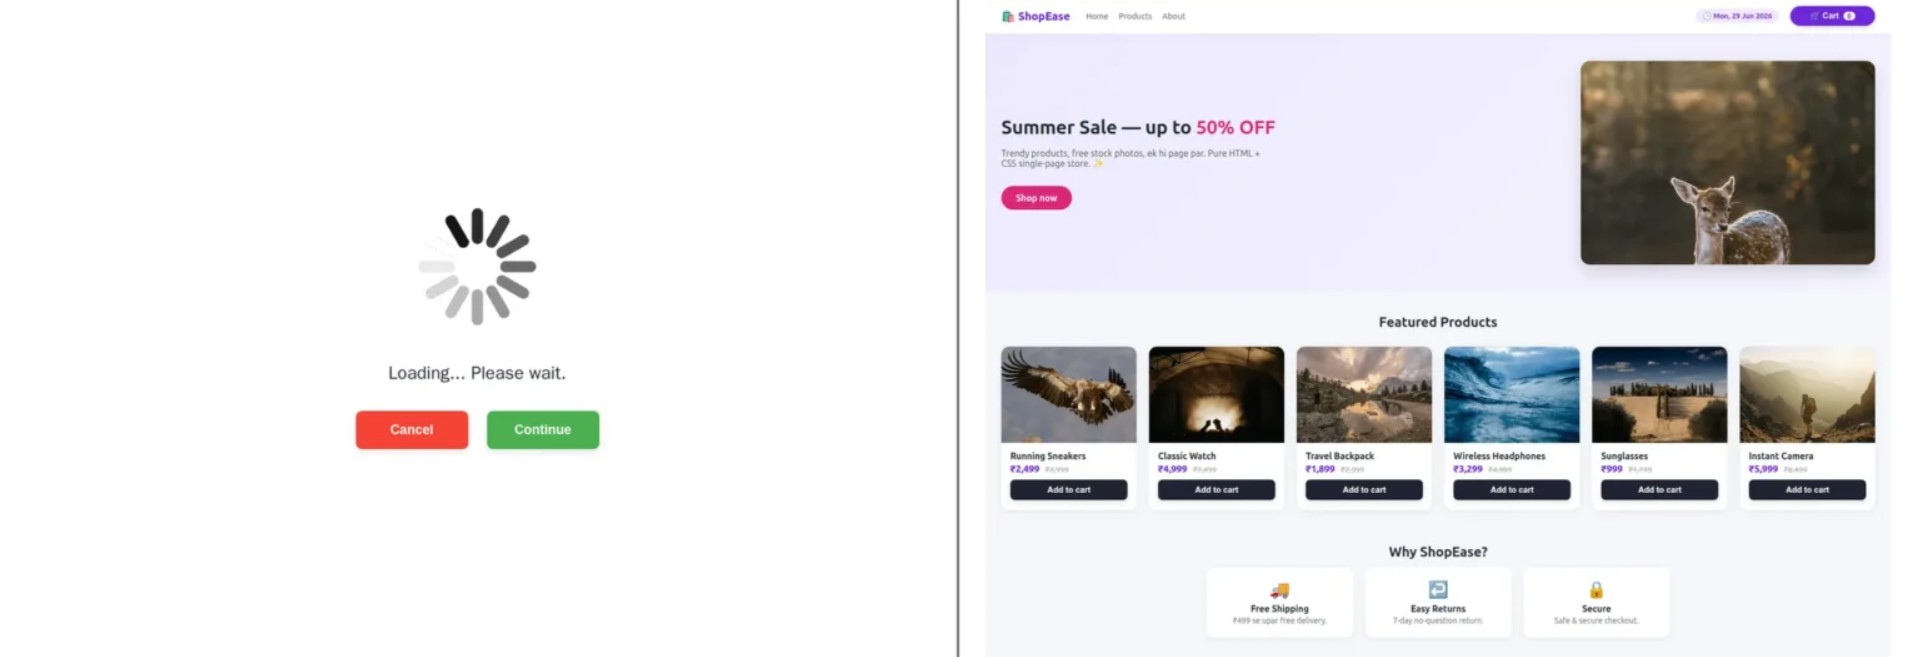
Note that the websites have not been hacked; the scammers are simply using their normal ad inventory. When you click on the ad, you first see a loading screen with a spinning GIF indicating that the page is still loading. However, researchers discovered that you wouldn’t see anything else until you move your mouse.
This is a check placed by the scammers to evade automated bot detection. Security companies regularly use bots to scan websites and catch scams like this. However, bots don’t move a mouse, so the page quietly waits until it detects mouse movement. Once you do that, you’re taken to another page that looks like a regular online shop called “ShopEase.”
Netskope
After you move your mouse, the page performs two decryption steps using hardcoded AES keys. It first decrypts a hidden string containing the address of the scammer’s server.
Next, it contacts that server and retrieves an encrypted payload tailored to the system you’re using, either Windows or Mac. The page then decrypts and assembles the fake warning inside the browser’s memory rather than downloading a separate locker file onto your computer.
What happens when the scam takes over your browser
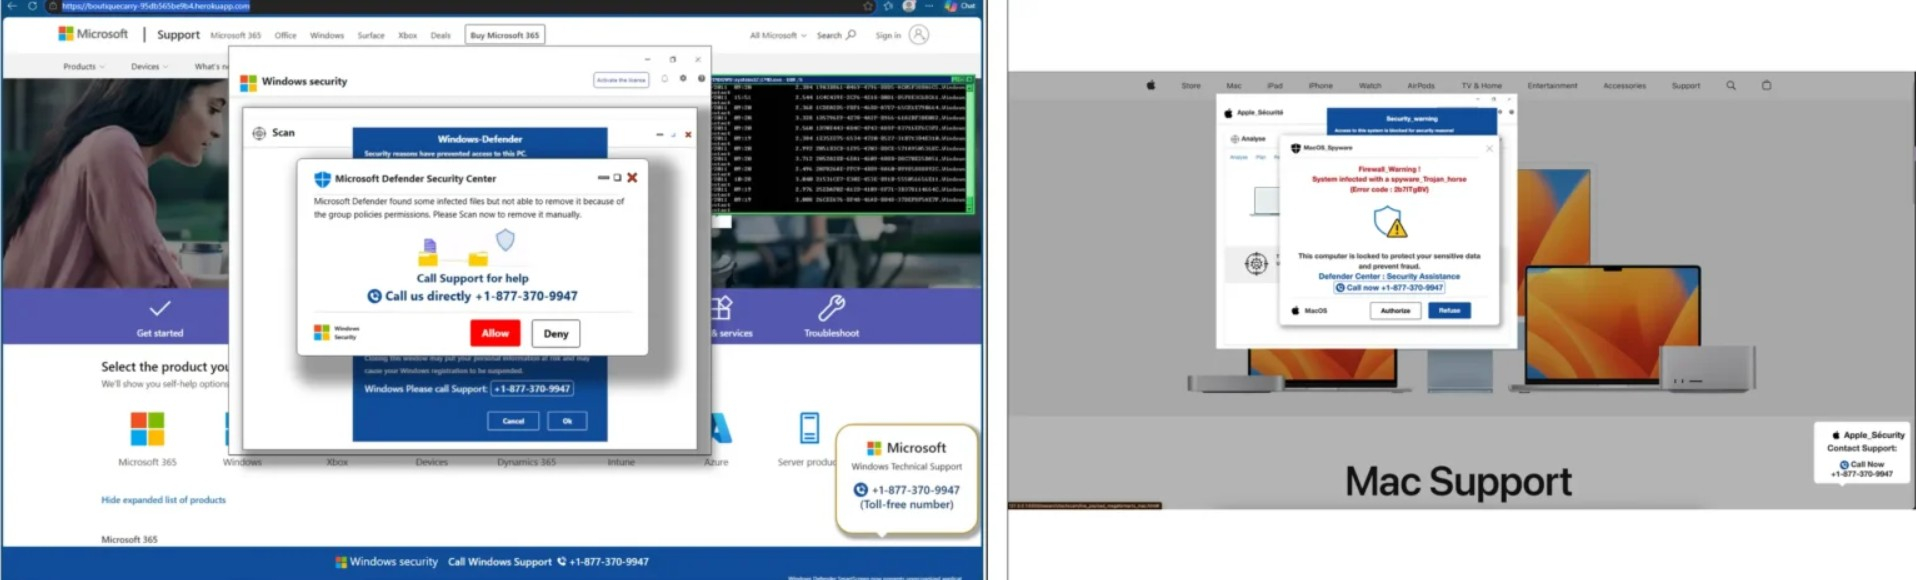
If you’re using Windows, you’ll see a fake Microsoft Defender Security Center scanning page, claiming that your computer is infected with malware, along with several stacked system dialog boxes and a callback number. On macOS, the scam uses a fake Apple storefront.
Netskope
Some other tactics it deploys:
The locker traps users in full-screen mode, hiding the address bar and tabs so that the fake warning can fill the whole screen.
It hides the mouse cursor and swallows the Escape key by calling the browser’s Keyboard Lock API, so that the user is struck with panic.
The page also plays alert sounds on interactions and runs busy loops, which makes the browser lag and makes the attack look more legitimate.
When in full-screen mode, victims also see a black lockout screen that reads, “Do not restart or operate the computer... call immediately.”
The page can also trigger the browser’s own confirmation dialog when you try to close the tab.
However, the computer itself isn’t actually locked, and operating system controls still work. All of these are social engineering methods and scare tactics designed to get the user to call the support number flashed on the screen.
Scammers use this method to launch a tech-support scam, where they can try to extract money, personal information, financial details, or even remote access to the computer. Giving away such sensitive information could lead to financial fraud, unauthorized charges on your credit cards, and even identity theft.
What can you do to protect yourself
This is a browser-level attack so simply opening the page doesn’t install malware on your operating system. The objective is to get you to call that number, allowing the scammers an opportunity to extract your personal information or money. This is why the attack is much easier to escape if you stay vigilant.
Never call any phone number shown in a pop-up: A legitimate operating system or browser will never lock your screen and demand that you call a phone number. If a webpage does this, treat it as a scam and do not call the number.
Exit full-screen mode: A quick tap of the Escape key won’t work because the locker has intercepted it. But press and hold it for a couple of seconds, and your browser should be forced out of full-screen mode. You can then close the tab showing the fake warning. If this doesn’t work, you can also force-close the browser by opening Task Manager on Windows with Ctrl + Shift + Esc, or Force Quit on Mac with Cmd + Option + Esc. Then reopen the browser without restoring the previous session.
Never share personal details with a caller: If someone claiming to be “tech support” asks for sensitive information such as credit card numbers, Social Security numbers, or other financial details after you encounter a warning like this, disconnect the call. The phone number displayed by the webpage isn’t proof that the caller works for Microsoft, Apple, or another legitimate company.
If you already called the number and shared personal information, such as your credit card details, call your financial institution immediately and block the card. Also, inform them of any unauthorized transactions you didn’t make. You could also choose to place a credit freeze with all three credit bureaus so that no one can open a new line of credit in your name.
Sharing such information can lead to identity theft, which is why it may also make sense to get an identity theft protection service. These tools can scan known breach databases and the dark web for your personally identifiable information and may help you restore your identity through professional restoration specialists.
Clicking on malicious links while browsing can sometimes lead to actual viruses or malware being downloaded onto your device. For protection against those threats, you’ll need a solid third-party antivirus program that scans downloads in real time and helps detect malicious files before they can harm your device.
The bottom line
The new Google Ads scam shows victims fake malware warning screens and stacked dialog boxes while displaying a callback number for an alleged tech-support team. However, waiting on the other side is a scammer attempting to extract personal information, money, or access to the computer.
While the attack page is designed to scare the victim, it operates at the browser level, so you can simply close your browser. Additionally, never call any number you see through an ad pop-up for tech support. Only reach out to the relevant company through its official channels.
Protect Every Aspect of Your Digital Life — Even Your Time
4.7
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Krishi Chowdhary specializes in digital privacy, cybersecurity, and consumer technology. He has written extensively on online privacy tools and broader cybersecurity topics, including online scams, data breaches, age verification, and emerging digital threats.
Krishi believes technology reporting should empower readers, not confuse them, and is committed to making even the most technical subjects easy to understand without compromising on accuracy or depth. His work has appeared in leading technology publications, including CNET, ExpressVPN, and TechRadar, where he has covered topics ranging from cybersecurity incidents and privacy product announcements to artificial intelligence and major technology news