We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
Typosquatting has long been a method scammers use to trick people into visiting fake websites that imitate legitimate ones. It involves using misspelled or lookalike domain names.
You land on what you believe to be a genuine shopping website or your bank’s portal, enter your credentials, and unknowingly hand them over to scammers. They could then use your login details to access your accounts, steal your personal information, or even drain your bank account.
Browsers have introduced safeguards to detect these deceptive domains, but researchers Ian Muscat and Leanne Briffa of Have I Been Squatted have now found that attackers can use two unusual characters to create lookalike domains that bypass key safeguards in Chrome and other Chromium-based browsers.[1]
Here’s how the trick works and what you can do to protect yourself.
Join thousands who get the latest security news, scams, and policy changes every week, right to their inbox.
By submitting this form you agree to receive emails from All About Cookies and to the
privacy policy and
terms.
Why Chromium’s defenses aren’t enough
Scammers want you to visit a fake website that looks like a genuine one. For instance, you might accidentally visit applle.com instead of apple.com.
To get around this, attackers can use letters from other alphabets that look almost identical to English characters. Russian Cyrillic, for example, contains several letters that resemble Latin characters, such as a, p, e, and o. Although they look similar, computers treat them as different characters.
According to Muscat and Briffa, two characters are particularly useful for bypassing browser safeguards: ө, found in languages such as Kazakh, Mongolian, and Tatar, and ƙ, a Latin letter with a hook used in Hausa and Karai-karai. These characters allow attackers to register deceptive domains such as oƙta.com instead of okta.com and niƙe.com instead of nike.com.
Browsers such as Chrome have safeguards designed to detect these tricks and display suspicious domains in a way that helps users spot the difference. However, the researchers found ways around several of these defenses.
Guardrail 1: All-Cyrillic lookalikes
In 2017, a researcher registered a fake Apple.com website using only Cyrillic letters. After this, browsers introduced a rule: if every letter in the domain name is Cyrillic and belongs to a known list of characters that look like English letters, the browser treats the domain as suspicious and displays it in its encoded form.
However, this rule is all or nothing. Even if one letter falls outside the predefined list, the check may not flag the domain. For example, researchers found that replacing the final е in the all-Cyrillic domain аррӏе.com with ө creates аррӏө.com, which can bypass this first guardrail because ө is not on Chromium’s Cyrillic lookalike list.
Guardrail 2: The famous website check
Chromium browsers maintain a list of 8,000+ popular domains. They simplify suspicious website addresses by stripping accents and converting lookalike characters into their English equivalents. If the resulting form matches a website on the list, the browser displays the address in its encoded Punycode form, which begins with xn--.
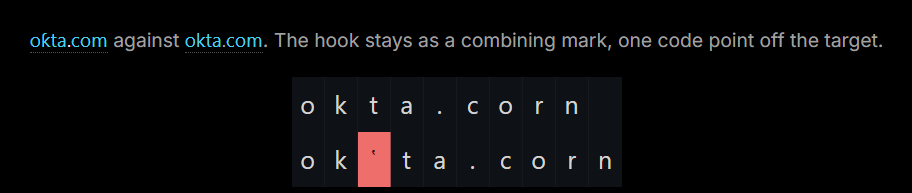
However, this guardrail also has a flaw. It strips accents before converting lookalike characters. Some characters, such as ƙ, have their hooks built in rather than added as an accent. When Chromium converts ƙ into k, the hook can remain as a separate mark.
Have I Been Squatted
As a result, oƙta.com does not reduce to an exact match for okta.com. The browser may therefore display oƙta.com in Unicode rather than its encoded form, leaving users without that potential warning.
Guardrail 3: The “Did you mean?” pop-up
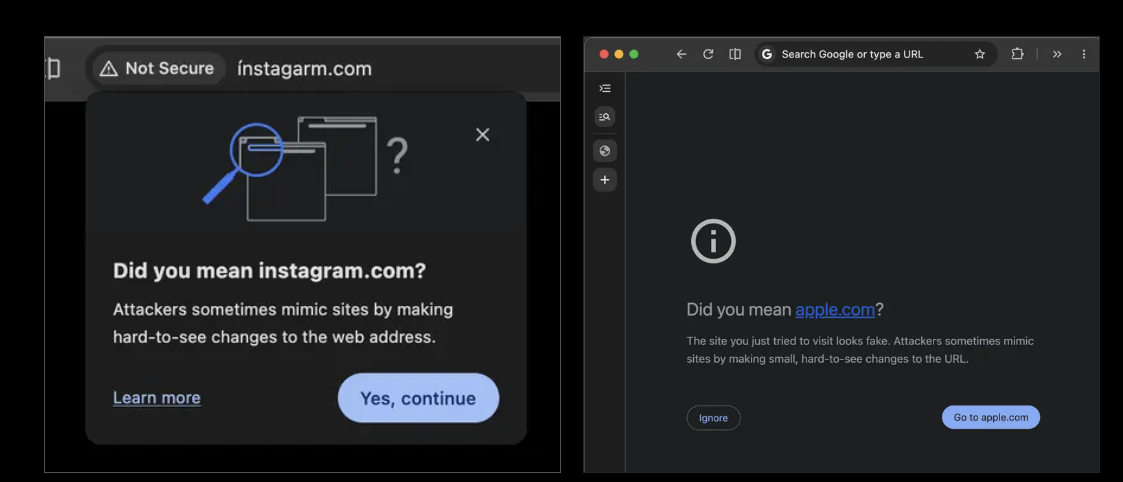
As another line of defense, Chrome can display a warning when you visit a website that closely resembles a popular domain or one you visit frequently. Depending on the match, this can take the form of a full-page warning or a smaller safety tip next to the address bar.
Have I Been Squatted
However, this safeguard also has limitations. Chrome checks for exact matches, single-character changes, and swaps between adjacent characters. It can miss domains that differ by two or more changes. It also skips near-match checks for domains with fewer than five characters before the top-level domain.
For example, the researchers found that аррӏө.com differs from Apple.com by two character changes after simplification, so it can evade the warning.
How typosquatting can put your personal data at risk
If you land on a fake website, you might inadvertently enter your username and password, allowing attackers to steal your credentials. They could also capture your two-factor authentication codes as you enter them and use the credentials and codes to authenticate a legitimate session from their own device.
This could be particularly damaging when visiting banking portals or social media websites, potentially allowing attackers to commit financial fraud or take over your accounts. Other threats include phishing scams and identity theft.
What can you do to protect yourself
The use of letters from other alphabets has made the age-old advice to “check the address bar” less reliable. It can be difficult for the average user to notice whether a website is genuine or spot a lookalike character replacing a letter in a familiar domain.
Here are a few steps you can take when visiting websites.
Go to websites directly: Use a saved bookmark or type the website address into your browser’s address bar. Avoid visiting websites through suspicious links or ads.
Use a strong password manager: Many reliable password managers come with an autofill function. They not only fill in your password but also match it to the correct website. So, if you accidentally visit niƙe.com instead of nike.com, your password manager’s autofill won’t work.
Switch to passkeys when possible: Like password managers, passkeys are tied to the legitimate website address, so they won’t authenticate you on a lookalike website.
Don’t trust the padlock icon: The padlock icon only means that your connection is encrypted. Fake websites can also obtain valid HTTPS certificates and display the padlock, so it’s not proof that a website is legitimate.
Watch for “xn--” in the address bar: If you see a website address starting with xn--, it may contain foreign characters encoded in Punycode. This isn’t always malicious, as legitimate websites may use such characters in their domain names. However, if you’re visiting a familiar website like Apple and see an unexpected xn-- address, treat it as a red flag.
Use an identity theft protection service: If you’ve already interacted with a fake website or shared your details, attackers could exploit that information in further scams.
The bottom line
Typosquatting has evolved beyond obvious misspellings. Attackers can now use lookalike characters from other alphabets to create deceptive websites that bypass certain browser safeguards and trick users into handing over sensitive information.
A successful attack could lead to stolen credentials, compromised accounts, financial fraud, or identity theft. Browser protections remain useful, but they’re not foolproof, so be careful when visiting unfamiliar websites and verify the address before sharing sensitive information.
4.5
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Krishi Chowdhary specializes in digital privacy, cybersecurity, and consumer technology. He has written extensively on online privacy tools and broader cybersecurity topics, including online scams, data breaches, age verification, and emerging digital threats.
Krishi believes technology reporting should empower readers, not confuse them, and is committed to making even the most technical subjects easy to understand without compromising on accuracy or depth. His work has appeared in leading technology publications, including CNET, ExpressVPN, and TechRadar, where he has covered topics ranging from cybersecurity incidents and privacy product announcements to artificial intelligence and major technology news