Account Takeover Is the Costliest Fraud Type, With 6 Million Victims in 2025
All About Cookies analyzed the latest account takeover fraud data from industry leaders to see how the crime is growing and which accounts are hijacked most often.
We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
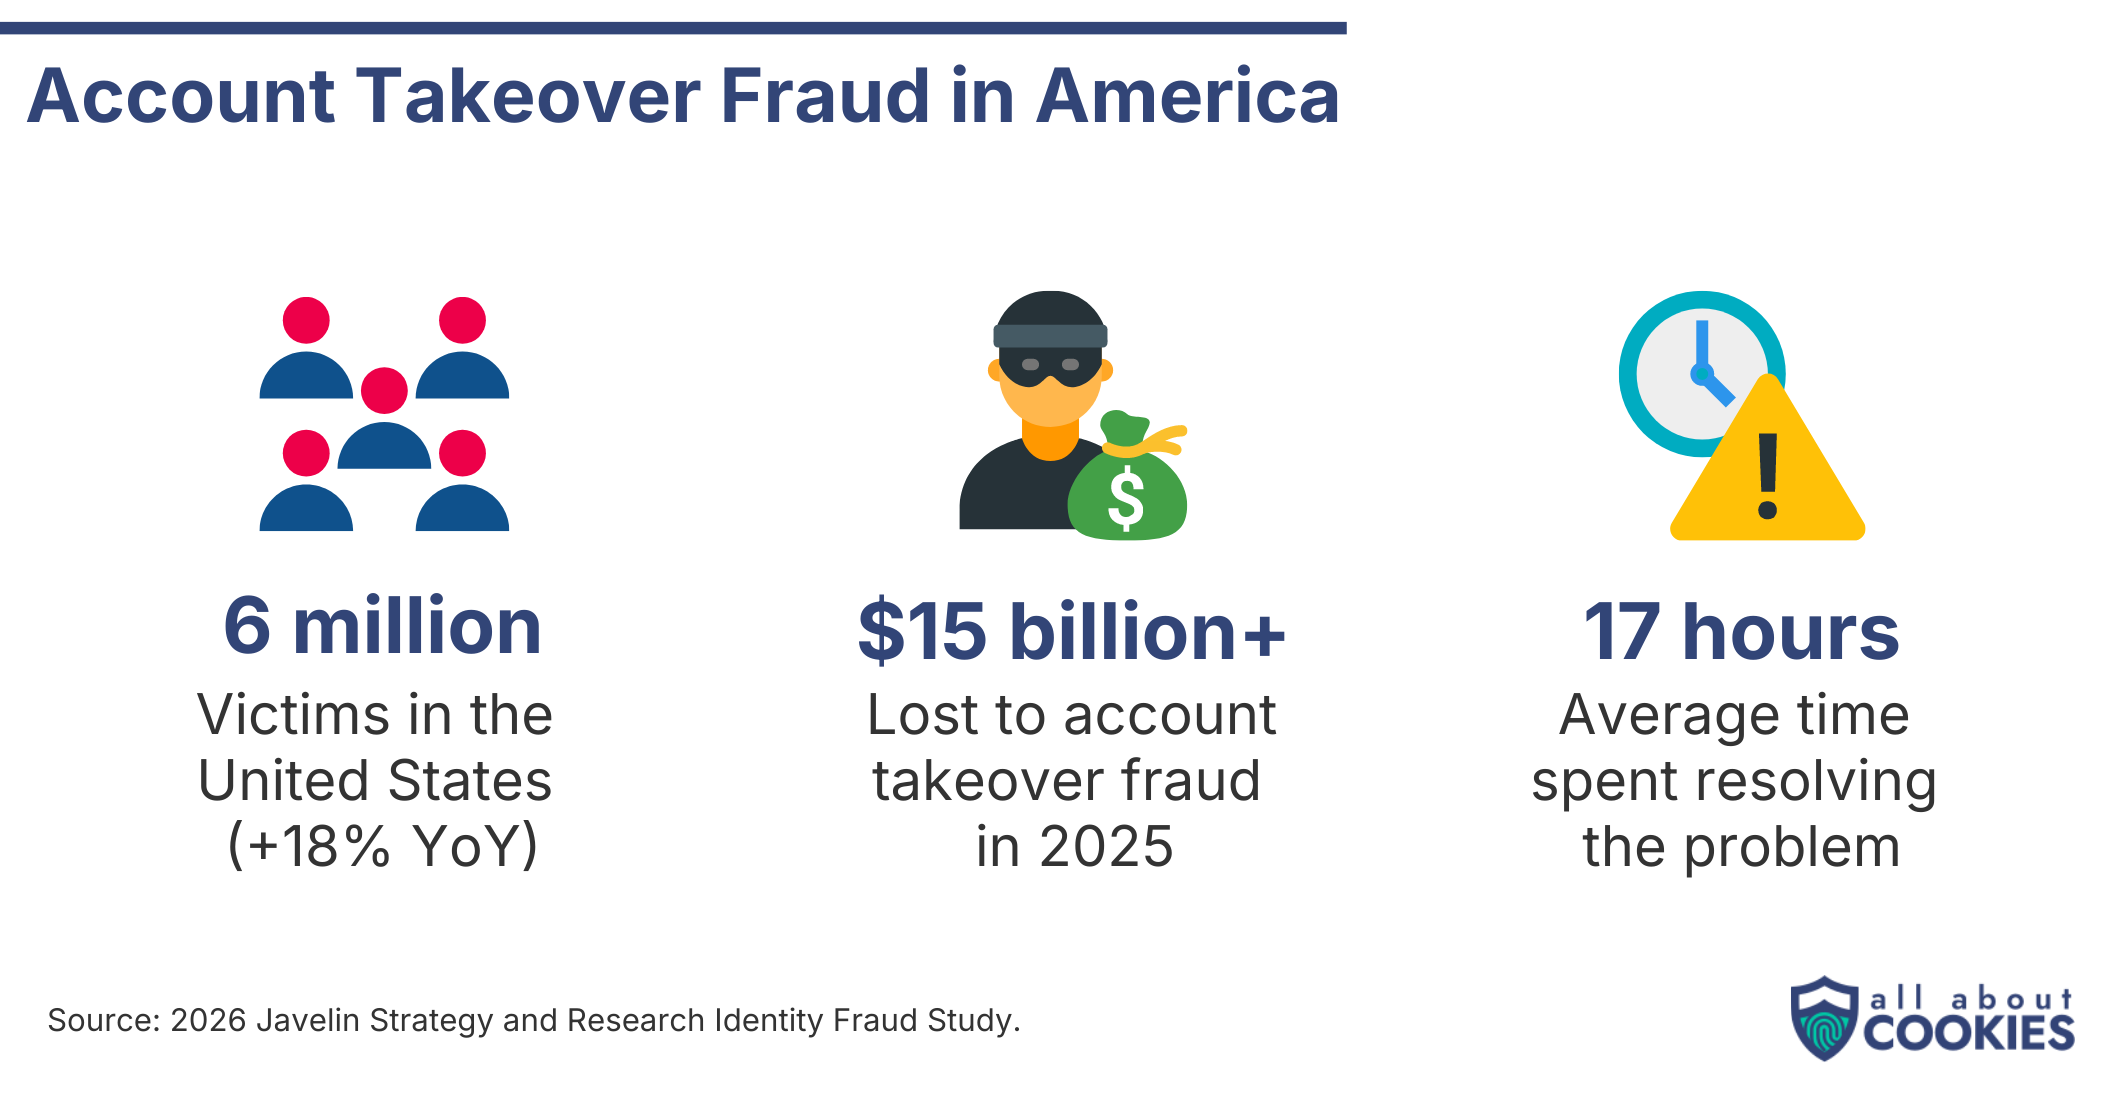
Six million U.S. consumers had an existing account hijacked by criminals in 2025. That's up 18% from 5.1 million in 2024, according to Javelin Strategy & Research's 2026 Identity Fraud Study.[1]
Account takeover (ATO) fraud happens when a criminal gets into someone's existing account, often a bank or email account, and uses it to steal money or information. ATO losses fell 4% last year but still topped $15 billion, making it the costliest fraud type Javelin tracks.
"Reduced losses do not mean reduced risk," said Suzanne Sando, lead analyst in Javelin's fraud management practice and author of the study.
The All About Cookies research team reviewed the latest ATO data from Javelin, the Federal Reserve, and Cloudflare to see who is being targeted and how.
6 million Americans had an account taken over in 2025, up 18% from 5.1 million in 2024.
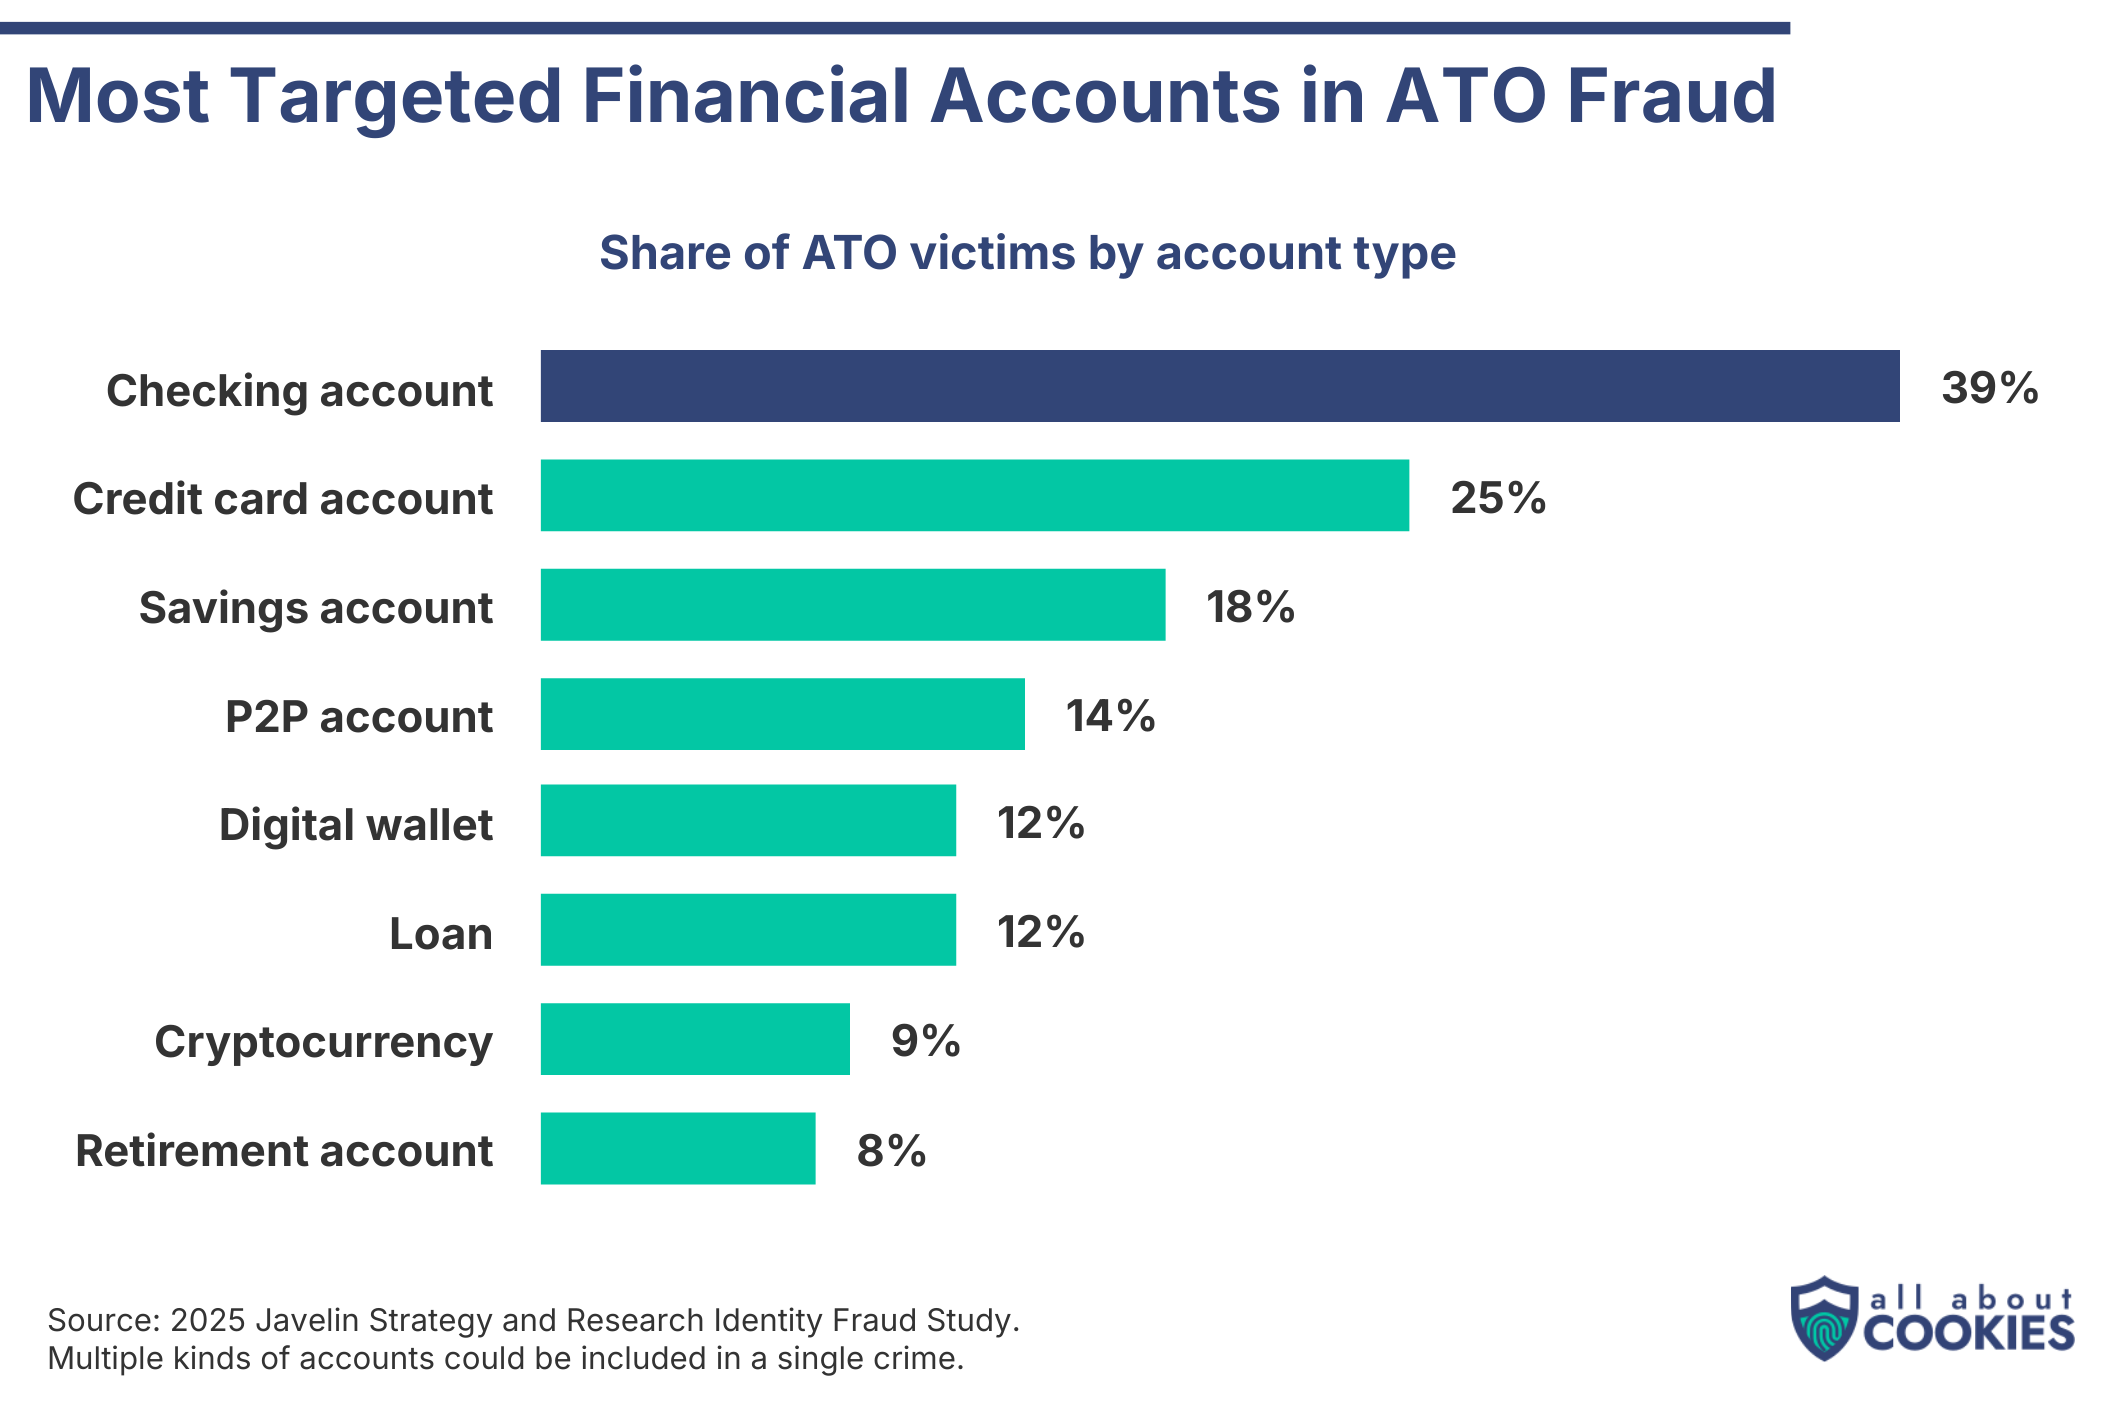
Checking accounts are the most common target, with 39% of victims saying their checking account was hacked.
Victims spent an average of 17 hours resolving account takeover fraud in 2025.
ATO fraud cost victims more than $15 billion in 2025.
Reports of account takeover increased 36% year over year, according to the most recent data published by the Federal Reserve.
Victims spend 17 hours cleaning up
ATO victims spent an average of 17 hours resolving the fraud in 2025, according to Javelin. That's well above the 10.4-hour average for identity fraud overall. Only victims of new-account fraud spent more time, at 17.8 hours.
Many victims also walk away from the institution involved. In 2024, 42% of ATO victims closed the account where the fraud happened, according to a June 2025 Javelin report. Fewer than 10% of victims said their financial institution was doing enough to protect them.
Checking and email accounts were top targets
Javelin's most recent breakdown by account type covers 2024. That year, 39% of ATO victims said their checking account was taken over, more than any other account type. Javelin notes that consumers often keep most of their available cash in checking, and those accounts are often linked to accounts at other banks and online merchants.
Credit card accounts (25%) and savings accounts (18%) came next, followed by peer-to-peer payment apps like Venmo and Zelle (14%) and digital wallets (12%).
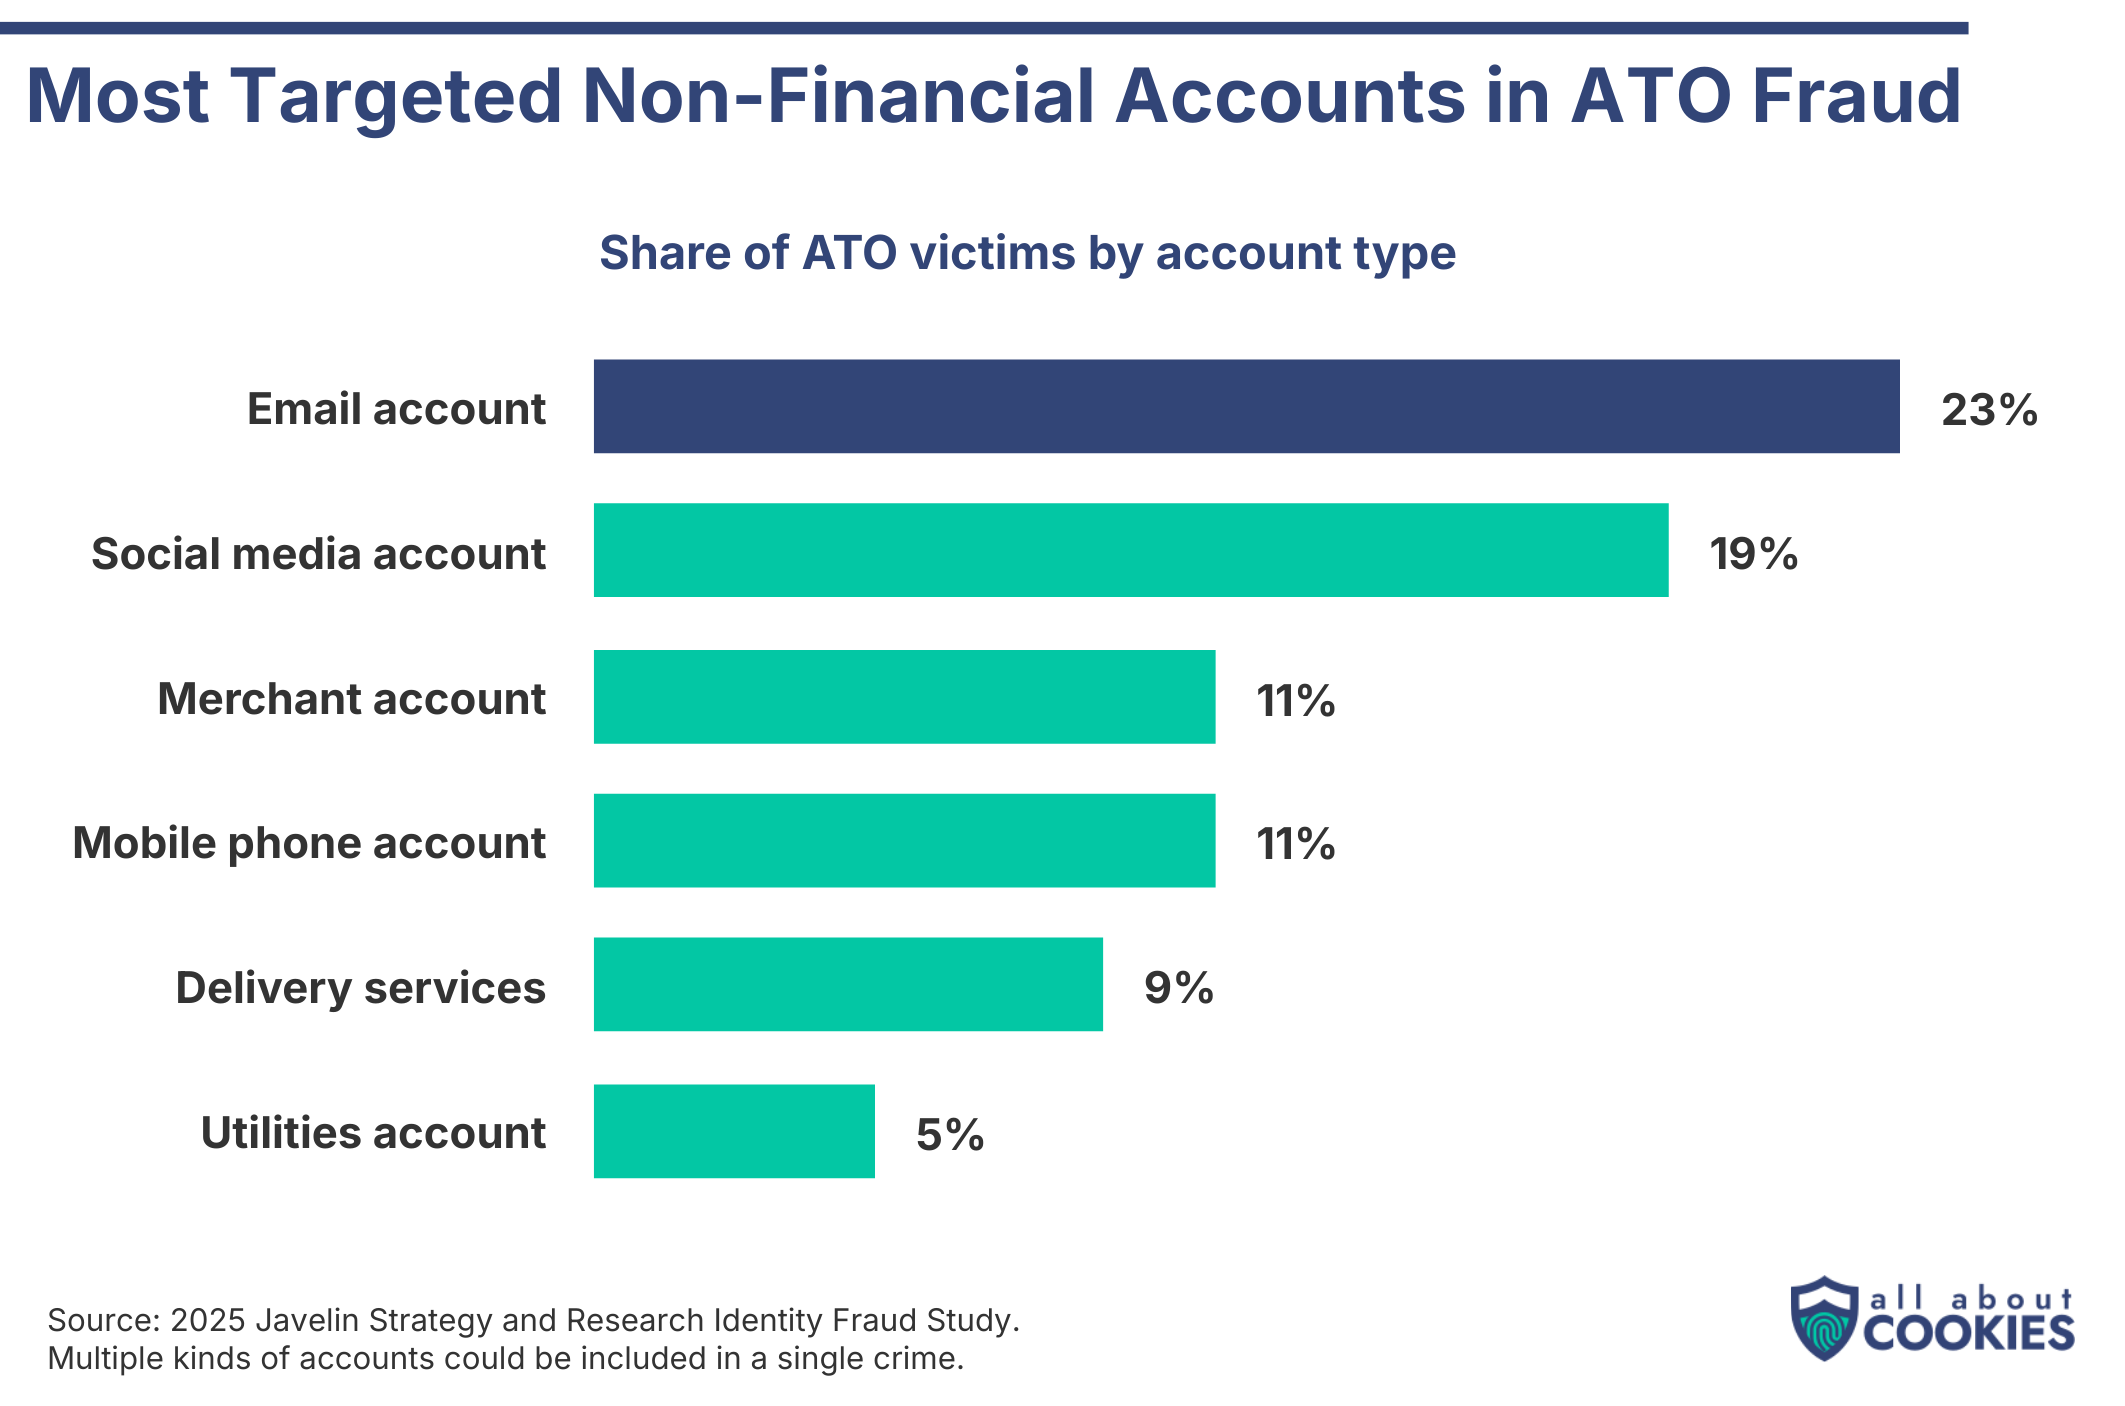
Non-financial accounts were targeted too. Email was the most common, with 23% of ATO victims reporting an email account takeover. Javelin notes that email accounts are linked to nearly all of a person's other accounts, so taking one over gives criminals a way into many others.
Social media accounts (19%), which hold personal and professional details, came next. Merchant accounts on sites like Amazon or Walmart (11%) followed, which often have saved credit cards attackers can use directly.
Reports of account takeover are climbing
Suspicious activity reports of account takeover filed with the Financial Crimes Enforcement Network (FinCEN) rose more than 36% from 2023 to 2024, the Federal Reserve reported in February.
The Fed pointed to three drivers: people's growing digital footprints, criminals' wider access to user data, and new tools that make account takeover easier to automate.
In March 2026, Cloudflare said its account takeover detections caught an average of 6.9 billion suspicious login attempts per day across its network over one week.
Common ways criminals get in include:
Credential stuffing: Bots test stolen username and password pairs across many sites. The Fed says data breaches and weak or reused passwords often make this work.
AI-powered scams: The Fed says generative AI lets criminals write polished phishing messages and create convincing deepfakes.
SIM swapping: Criminals persuade a phone carrier to move a victim's number to a SIM card they control, then intercept one-time passcodes sent by text.
How to protect your accounts from takeover
Use a password manager. Reused passwords let one breach unlock several accounts. A password manager creates and stores a unique login for every account.
Turn on two-factor authentication. The Fed calls multifactor authentication "a foundational prevention tool." Where possible, choose an authenticator app or passkey over text codes, which SIM swaps can intercept. Learn how two-factor authentication works.
Check whether your data has been leaked. Credentials stolen in past breaches fuel credential stuffing, so knowing what's exposed tells you which passwords to change.
Use a VPN on public Wi-Fi. Javelin lists man-in-the-middle attacks, which intercept data in transit, as one route to account takeover. A VPN encrypts your traffic on shared networks.
Watch for small account changes. Javelin says early warning signs can be subtle, like a new name, email address, or phone number added to your account.
Consider identity theft protection. With victims spending 17 hours on average cleaning up, an identity theft protection service can flag leaked data and suspicious activity early.
4.8
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Steph Trejos is a Certified Anti-Money Laundering Specialist (CAMS), a credential that reflects deep expertise in financial crime, fraud patterns, and cyber threats. As a Senior Product Testing Editor at All About Cookies, she has personally evaluated nearly 200 digital security products and brings that forensic rigor to every review she oversees. Before joining AAC, she produced publications on financial crime and cyber threats at ACAMS.