WordPress Security: 8 Ways To Protect Your Website
You don't need to be a security expert to protect your WordPress site. Start with these eight practical steps to keep hackers out and your website running safely.
We receive compensation from the products and services mentioned in
this story, but the opinions are the
author's own. Compensation may impact where offers appear. We have not included all available products or offers.
Learn more about
how we make money
and
our editorial policies.
Advertiser Disclosure
All About Cookies is an independent, advertising-supported website. Some of the offers that appear on this
site are from third-party advertisers from which All About Cookies receives compensation. This compensation
may impact how and where products appear on this site (including, for example, the order in which they
appear).
All About Cookies does not include all financial or credit offers that might be available to consumers nor
do
we include all companies or all available products. Information is accurate as of the publishing date and
has
not been provided or endorsed by the advertiser.
Close
Editorial Policy
The All About Cookies editorial team strives to provide accurate, in-depth information and reviews to help
you, our reader, make online privacy decisions with confidence. Here's what you can expect from us:
All About Cookies makes money when you click the links on our site to some of the products and offers that
we mention. These partnerships do not influence our opinions or recommendations. Read more about how we
make money.
Partners are not able to review or request changes to our content except for compliance reasons.
We aim to make sure everything on our site is up-to-date and accurate as of the publishing date, but we
cannot guarantee we haven't missed something. It's your responsibility to double-check all information
before making any decision. If you spot something that looks wrong, please let us know.
Close
Most people who own or manage a WordPress site understand the importance of WordPress security on some level, but far fewer understand the devil in the details. One common misconception is that protecting your site only requires the bare minimum: keep WordPress, plugins, and themes up to date, and maybe install a security plugin.
Those basic steps cover a lot of ground, but they still leave plenty to cover. Hardening a WordPress site also means choosing a reliable host, configuring user access, creating strong passwords, and backing up regularly.
You don't need to understand every technical vulnerability to start protecting your site. I'll start with eight practical WordPress security steps you can take, then explain the research behind them and what to do if your website gets hacked. Let's get started.
Join thousands who get our privacy-first newsletter every week. No spam. No nonsense.
By submitting this form you agree to receive emails from All About Cookies and to the
privacy policy and
terms.
WordPress security checklist: 8 ways to protect your site
You don't have to become a security expert to make your WordPress site safer. Start by keeping your software updated, protecting your logins, reviewing access, and ensuring you have a working backup. The eight steps below cover those basics and the additional protections worth checking.
1. Keep WordPress, plugins, and themes updated
WordPress plugins account for most reported vulnerabilities, so keeping them updated is especially important. That doesn't mean you shouldn't use themes or plugins, but it does mean three things:
Monitor your WordPress admin dashboard or activate notifications to be pinged when a developer releases a new version of any plugin or theme on your site. Then update accordingly, and preferably one item at a time in case anything breaks. You can also enable auto-updates, which can help close security gaps faster. If you manage updates yourself, check regularly and prioritize security fixes. For sites where compatibility is a concern, a managed WordPress host may handle updates and test for problems.
Deactivate and remove any unused themes or plugins. There's no point in leaving a potential target sitting on your site when it's not doing anything for you.
If you're using an abandoned (by the developer) plugin on your site, see if you can find an actively maintained equivalent. If you can't or don't want to switch, at least check if the plugin has been flagged for security issues. Start with the plugin's official page in the WordPress repository, and then cross-reference with Patchstack, Wordfence, and WPScan. All three have searchable databases.
The World's Most Popular Website Builder, Now With Managed Everything
4.5
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
PROMOTION: Up to 69% Off Select Plans + Free Migration
Everything managed for you — automated updates, real-time backups, and security built in from day one
Unified wp-admin dashboard removes the dual learning curve of separate hosting and site-building tools
Enterprise-grade security stack — CDN, malware removal, DDoS protection, and a WAF — included on every plan, even free
2. Choose plugins and themes carefully
When it comes to themes and plugins, don't install a plugin just because it fills a need on your website. This has always been good advice, but in the modern AI era, it matters even more. AI coding tools have made it possible for anyone, regardless of knowledge or experience, to vibe code a plugin. This is actually a good thing because it has democratized software development, but from a pure security lens, it introduces new layers of risk.
If you come across such homemade plugins on random blogs, be cautious about downloading them. You have no idea what vulnerabilities they might contain, and depending on the developer, they might not know either.
To reduce the risk of harm to your WordPress site, download themes or plugins from the official WordPress repository whenever possible. For premium-only plugins not available in the repository, research the developer before paying and downloading any installation files.
3. Use strong passwords and enable two-factor authentication
You probably already use a strong password for your WordPress site, but reusing it across multiple sites can trigger a damaging domino effect. A single leak can expose every place you reused that password. That's why it's better to keep your logins separate. The most practical solution is a password manager.
In addition, setting up two-factor authentication (2FA) or multi-factor authentication (MFA) adds another layer of protection against stolen passwords and unauthorized logins. Even if an attacker gets your password, they'll still need to pass the additional authentication check.
Most security plugins like Wordfence or Titan have a built-in 2FA feature you can activate. They also offer tools to limit how many wrong-password attempts someone can make within a set time period before they are locked out. Combine the above, and you'll make it considerably harder for hackers to break into your WordPress site.
4. Limit administrator access and user permissions
WordPress includes predefined user roles, each with its own permissions. A standard single-site installation has five main roles, while WordPress Multisite also includes Super Admin. If more than one person logs in to your website, be mindful of how you assign user roles.
Take, for example, a multi-writer WordPress blog where you regularly have various writers producing blog posts. Those writers should be assigned either a Contributor role or an Author role. Anything above that is unnecessary for routine writing tasks and exposes the blog to unnecessary risk.
In short, when approving new accounts, assign user roles based on what each individual needs to complete their work. Also, review user accounts periodically and remove any stale accounts to keep your user base clean.
5. Choose secure WordPress hosting
Protecting your WordPress site from hackers takes teamwork. You manage the website, while your web hosting provider manages the server it runs on. Exactly how those responsibilities are divided depends on whether your hosting is managed or unmanaged.
When evaluating hosts, look for security features like DDoS protection, a web application firewall (WAF), malware scanning and removal, a free SSL certificate, uptime monitoring, and automatic backups. These will give your WordPress site a solid security base.
If you already have WordPress hosting but realize it lacks crucial security features after reading this, consider switching to a new host. Check out my roundup of the best WordPress hosts for some ideas.
4.9
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Web hosting built around WordPress, with an AI site builder included on every plan
Free SSL, CDN, and domain (first year) come with every plan, no upgrade required
Plans start at $2.37/mo, with a 30-day money-back guarantee if it's not the right fit
6. Protect your website with HTTPS
Unlike plain HTTP, HTTPS encrypts data transmission between a website and its visitors, helping prevent someone who intercepts that traffic from reading sensitive information like passwords, messages, or credit card info.
Some web hosts even have a "force HTTPS" toggle that you can switch on, which forces your website to be served as https://yoursite.com even if a visitor types in yoursite.com, www.yoursite.com, http://yoursite.com, or any other non-HTTPS version.
Before you can activate that, you first need an SSL certificate. An SSL certificate helps authenticate your website's identity and enables encrypted HTTPS connections. It's basically like having someone vouch that you are who you say you are. Most web hosts include these for free. If yours doesn't, you can get one (for free) from Let's Encrypt or buy a premium version.
7. Use a firewall and monitor for threats
A web application firewall (WAF) protects web applications by filtering and monitoring HTTP/HTTPS traffic. Unlike traditional firewalls that focus on network-layer traffic, it operates at the application layer and specifically targets web-based threats, including many of the vulnerabilities discussed later in this guide.
Security monitoring is a non-specific term that can loosely refer to several WordPress security solutions. Malware scanning is often part of it, but some of the best web hosting services add automatic malware removal on top of the scanning. Scanning helps detect threats, while removal is a separate step that may require additional tools or support.
By choosing a WordPress hosting plan that includes both a WAF and security monitoring, you can strengthen your malware prevention and detection strategy.
8. Back up your WordPress site
Securing your WordPress site is primarily about reducing the odds of an attacker hacking it. That's plan A, and if you do it right, you may never need plan B. Prepare one anyway. Here's why: You can follow all the best WordPress security practices, but you can't predict the future. If, by some great misfortune, you get hacked, you'll want a recent, uninfected version of your site to restore. That's what a backup does.
Choose a host that backs up your site automatically and keeps backups for a long time. For a site that changes frequently, daily or more frequent backups may be appropriate. A less active website may need fewer backups.
Make sure your backups include both your WordPress files and database, and test the restoration process periodically. A backup is only useful if you can actually recover your site from it.
4.8
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Web hosting built around WordPress, with a dashboard our tester called the best they'd used for a WordPress host
100% uptime guarantee confirmed in testing, with daily automated backups and one-click restore
Free SSL and domain (first year) included on all plans, starting at $2.89/mo
Why WordPress security matters
Now that you know the steps you can take to protect your WordPress site, let's look at why those protections matter. The research below shows how WordPress vulnerabilities have changed over time and why keeping your software updated matters.
You probably already understand that WordPress security matters, but here are some concrete ways an attacker or group of attackers could harm your site. The fallout could include any of the following:
Website defacement
Malicious redirects
SEO spam (spamdexing)
Malware distribution
Resource hijacking
Data breach
Financial theft and phishing
Complete server takeover
This is not an exhaustive list, and not all of the above carry the same weight. The list starts with arguably the least harmful option and gets progressively worse as you move down. The outcomes depend on the specifics of each attack, including what it targeted, which isn't limited to WordPress core (i.e., the files that run the main WordPress software).
WordPress core is generally less exposed to reported vulnerabilities than the plugins and themes you install, especially when you keep it updated to the latest version. I'll explain why in the next section, but first let me share some of the latest WordPress security data from Patchstack, which is one of the leaders in this space.
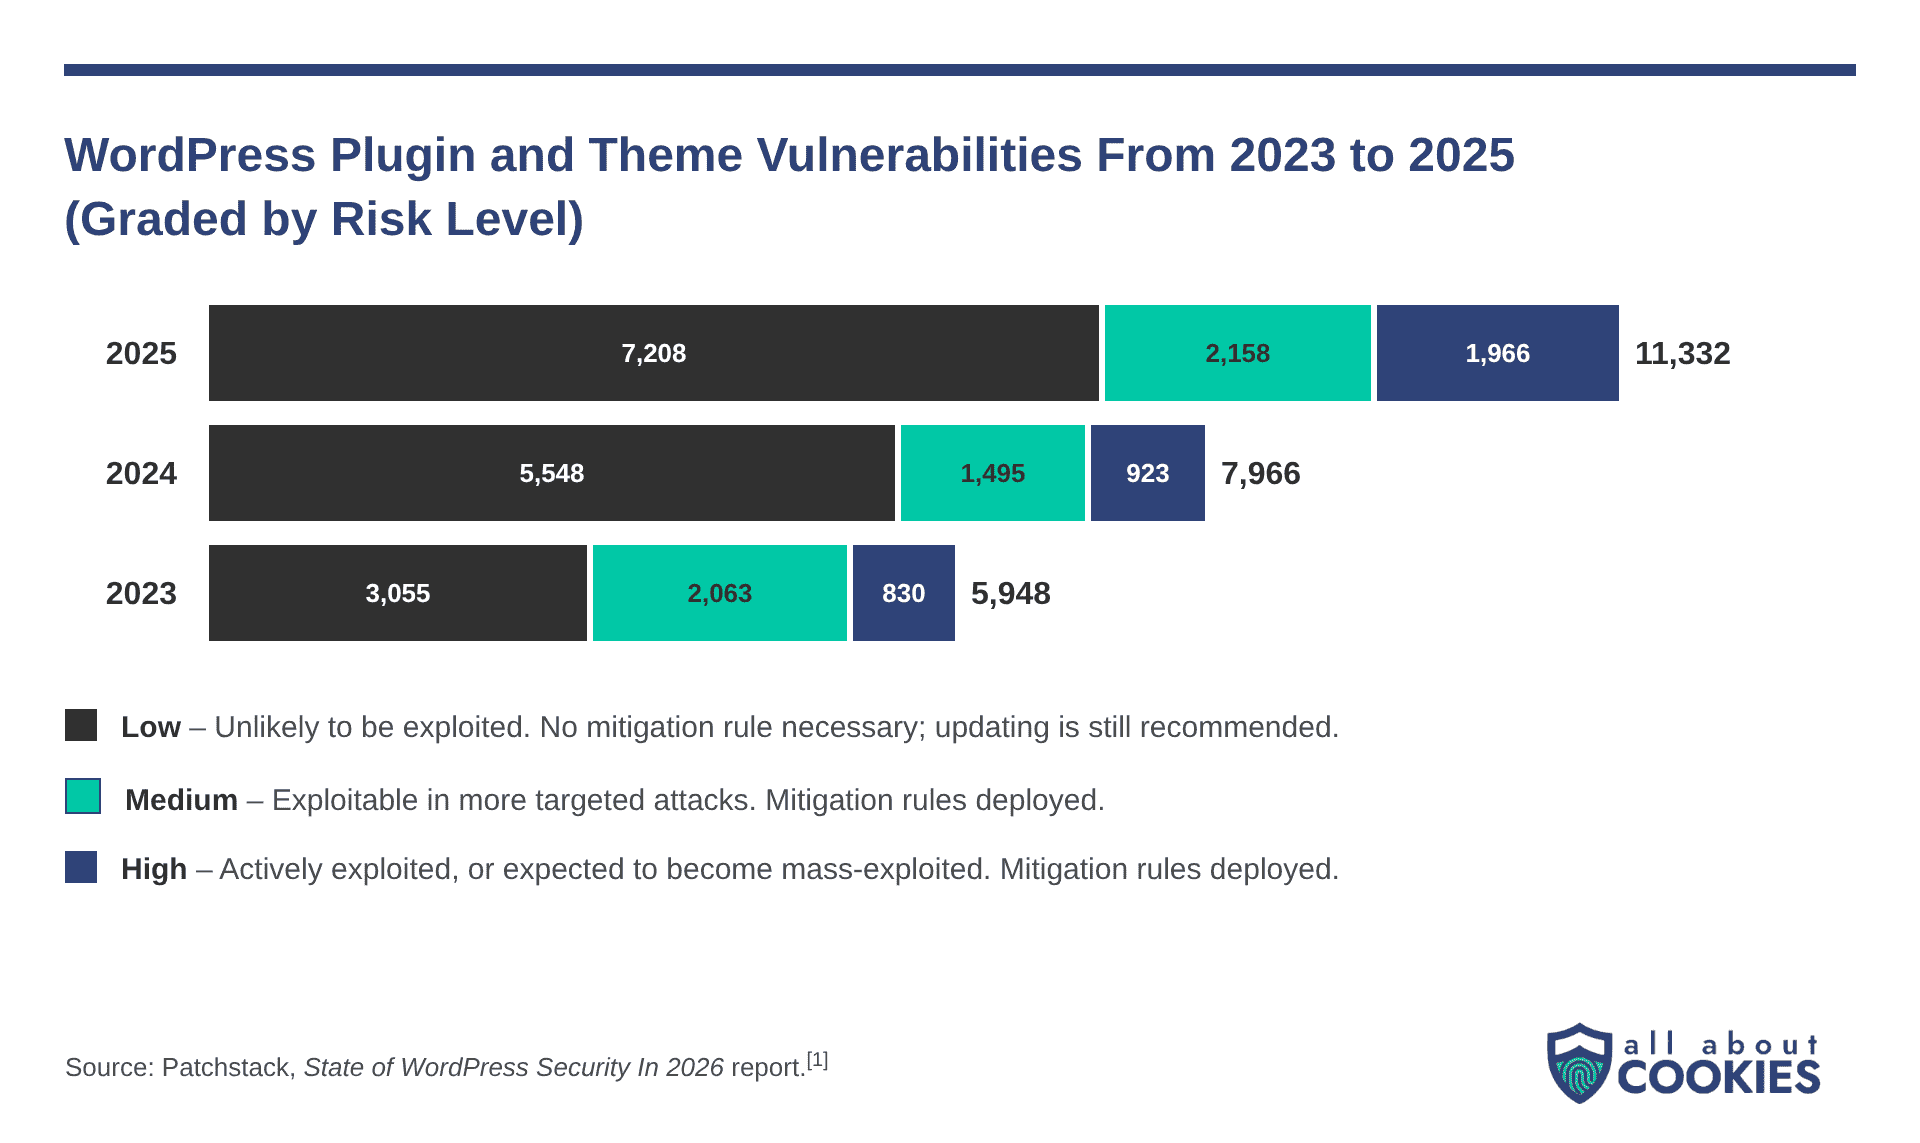
In its State of WordPress Security 2026 report, Patchstack found that between 2023 and 2025, the number of new vulnerabilities discovered in WordPress themes and plugins nearly doubled. Within the high-severity group, it more than doubled over the same period, with the biggest jump in a single year — from 923 in 2024 to 1,966 in 2025.
Bar chart comparing reported WordPress plugin and theme vulnerabilities by severity from 2023 to 2025.
(Mitigation rules refer to Patchstack's in-house solutions to address the threat from vulnerabilities.)
What this means for you: More vulnerabilities are being discovered in WordPress plugins and themes, making regular updates and careful plugin selection especially important.
This demonstrates that reported vulnerabilities in the WordPress ecosystem have increased significantly and that WordPress security should never be an afterthought. However, we also need to be honest about what these numbers represent and what they don't. They are opportunities to attack, not actual attacks. For data on actual attacks, Patchstack found that during testing, approximately half of high-impact vulnerabilities were exploited within 24 hours of being publicly disclosed.[1]
That's the more concerning statistic, but it also doesn't mean you need to panic. We're talking about a figure in the high hundreds for an entire year measured against more than 37.2 million live WordPress sites.[2]
Those figures don't tell us how likely any individual website is to be hacked. At the same time, they're not a green light to throw caution to the wind. The threat is real, and though we'll never eliminate it, understanding the risks can help us mitigate them as much as possible. Let's talk about those risks next.
Common WordPress security risks
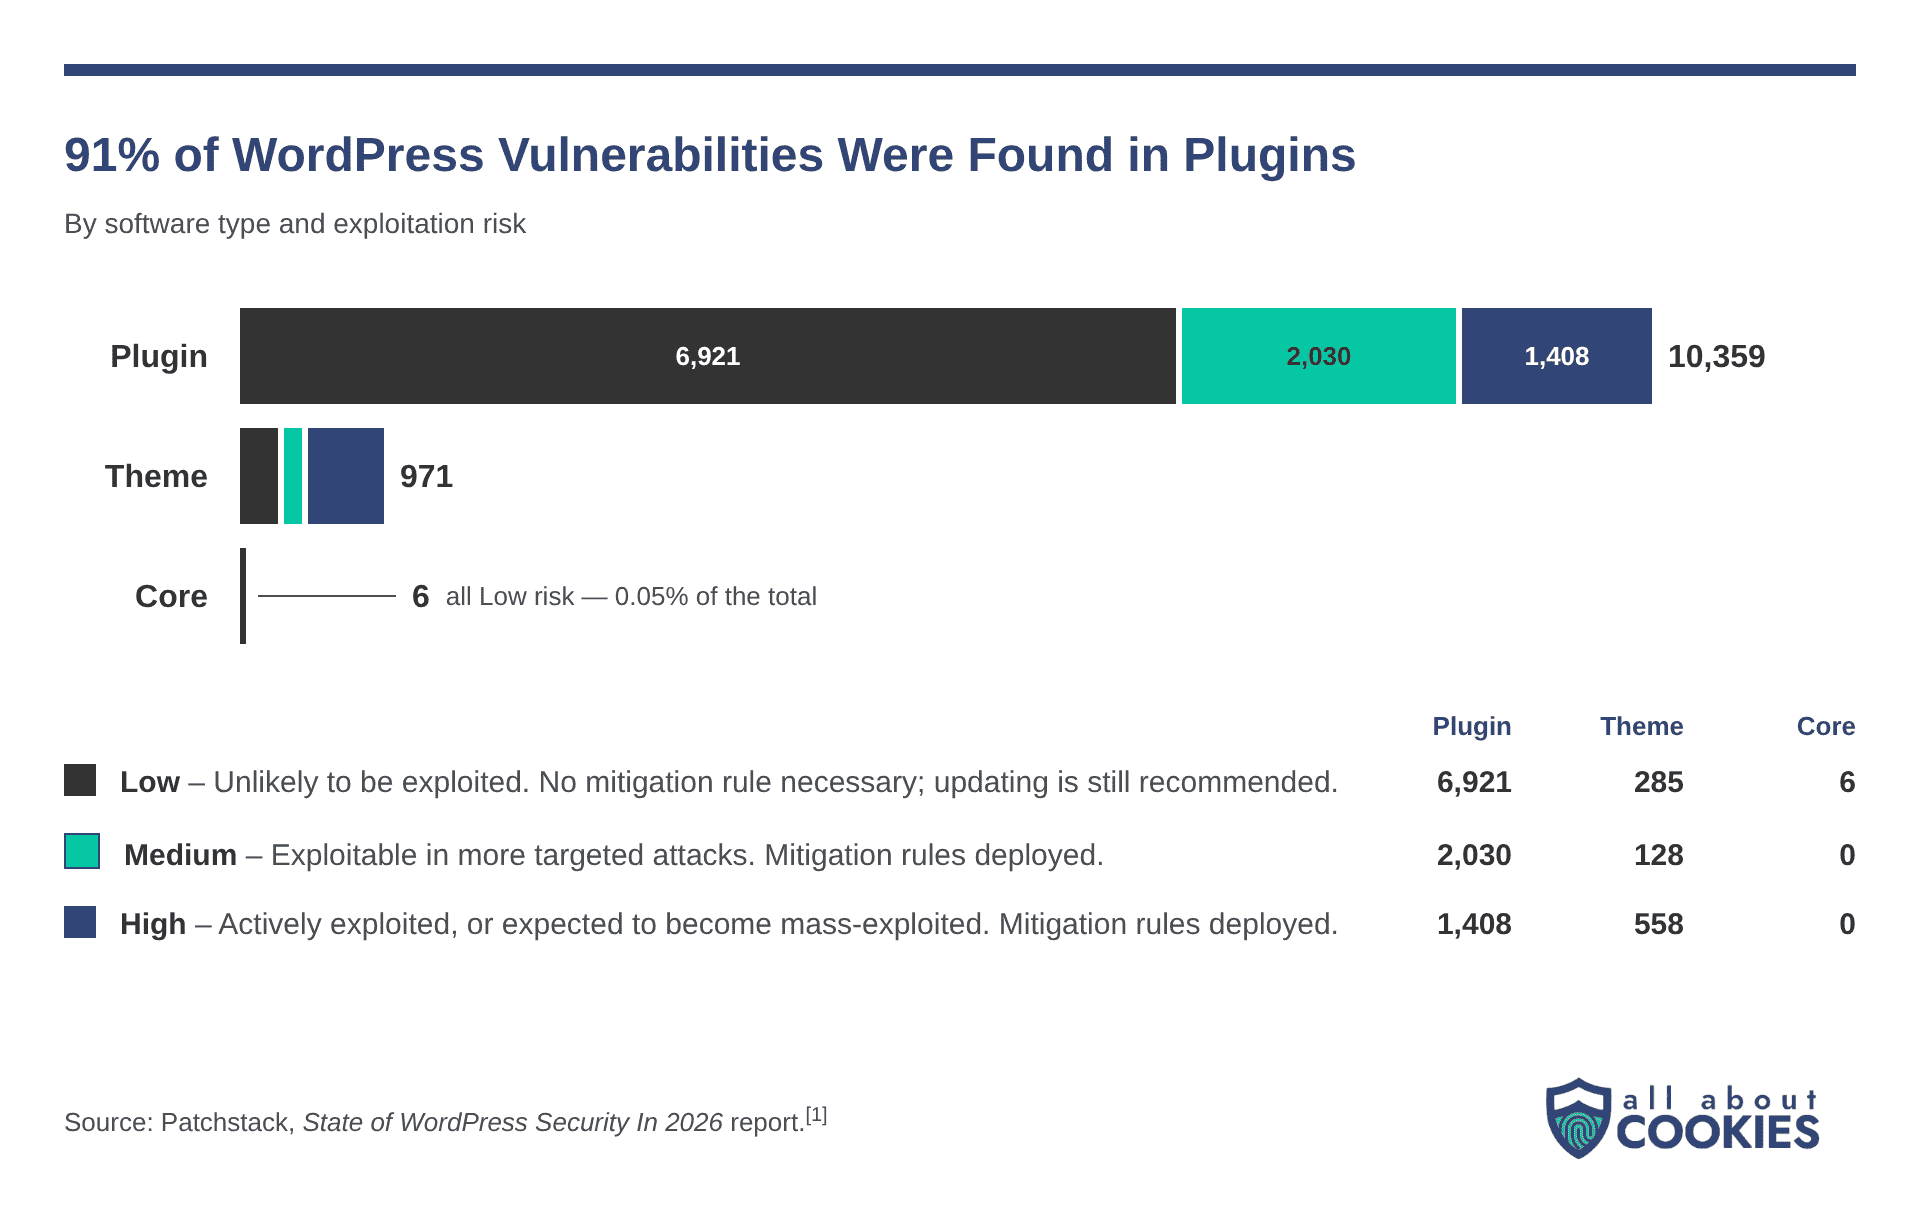
Earlier I mentioned that WordPress core accounts for relatively few reported vulnerabilities compared to plugins and themes. The numbers below explain why:
Chart showing the distribution of reported WordPress vulnerabilities across plugins, themes, and WordPress core in 2025.
What this means for you: The overwhelming majority of vulnerabilities reported in 2025 involved plugins rather than WordPress core. The plugins you install deserve just as much attention as WordPress itself.
In 2025, 11,336* newly discovered vulnerabilities appeared across the WordPress ecosystem, but only six were found in WordPress core.That's only about 0.053%. Not exactly an alarming number. Not to mention, all six were labeled low priority. In contrast, approximately 9% of new vulnerabilities were found in themes, while 91% were found in plugins, making plugins by far the biggest attack surface.[1]
(*There is a four-count discrepancy in Patchstack's reporting between this 2025 dataset and the dataset in the previous section that refers to the same statistic. This presentation put the 2025 total vulnerabilities at 11,336, while the previous one had it at 11,332.)
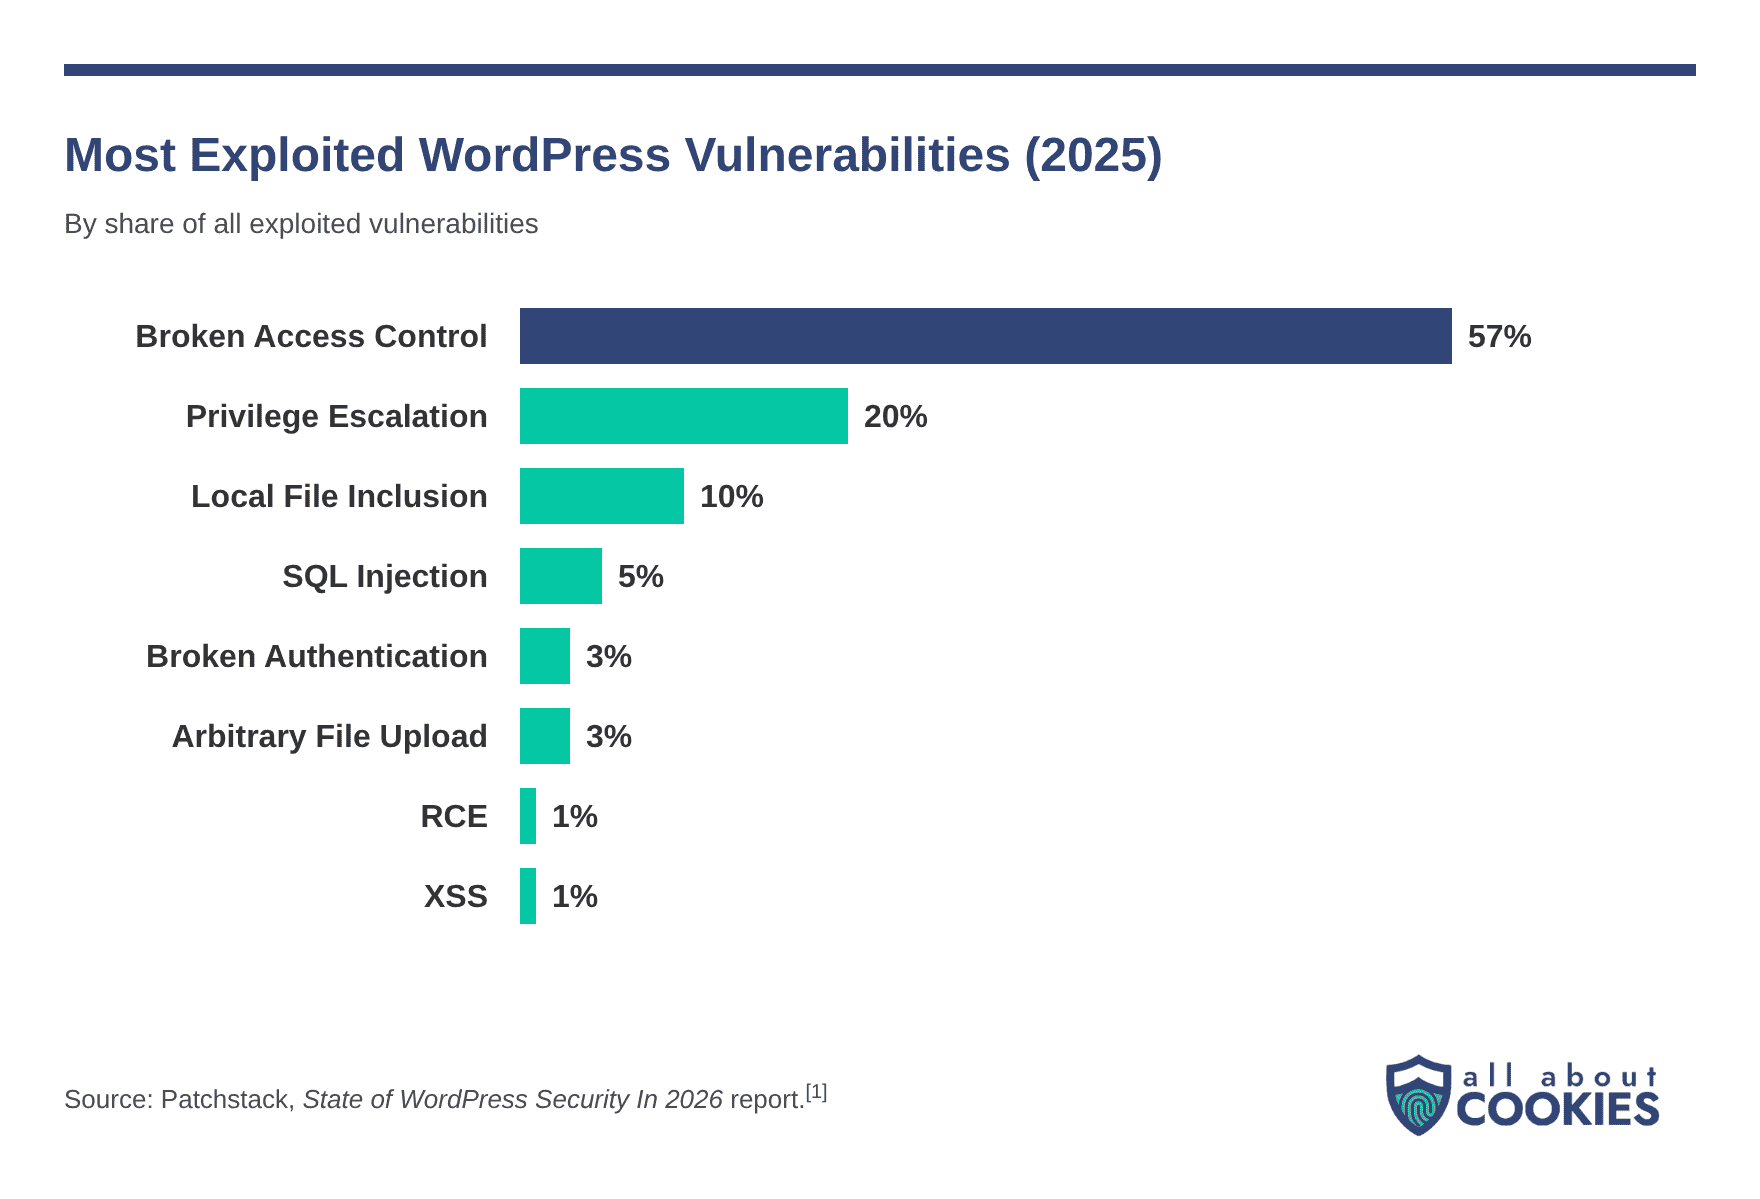
Of all the identified vulnerabilities, the three most exploited were broken access control, privilege escalation, and local file inclusion. The full breakdown is as follows:
Bar chart showing the most exploited WordPress vulnerability types in 2025, including broken access control, privilege escalation, and local file inclusion.
What this means for you: Attackers don't always need to guess your password. Plugin and permission vulnerabilities can also let them access parts of your website they shouldn't control.
How do these WordPress vulnerabilities translate into real-world risks?
In other words, what behaviors or software weaknesses can lead to a WordPress site owner becoming a victim of broken access control or SQL injection?
Here's the breakdown:
Risk #1: Plugins with unsafe permissions. If a plugin implements custom actions but forgets to verify whether the current user has permission to perform them, a lower-privileged user can run administrator tasks. This is a classic example of broken access control that can lead to privilege escalation.
Risk #2: Outdated or abandoned software. Using vulnerable or abandoned plugins, themes, or outdated WordPress core is a common entry point for complex technical attacks. These vulnerabilities include cross-site scripting (XSS), SQL injection (SQLi), local file inclusion, arbitrary file upload, and remote code execution (RCE).
Risk #3: Repeated login attempts. Failing to configure your website to resist brute-force attacks is one of the easiest security risks to address, as discussed in the best practices section. Without protections such as login attempt limits and 2FA, attackers have more opportunities to exploit weak authentication and gain unauthorized access.
Risk #4: Weak or stolen passwords. Weak or reused administrator credentials, or stolen administrator credentials, can let attackers sign in as an authorized user. If the compromised account has administrator privileges, the attacker may gain extensive control over the website.
Risk #5: Insecure shared hosting. If a shared hosting provider doesn't properly isolate websites, an attacker who compromises another site on the same server may exploit server-level weaknesses. Depending on the vulnerability, that could expose files such as wp-config.php, allow access to databases, or let an attacker overwrite files or inject malware. Basically, attackers may bypass WordPress entirely by exploiting weaknesses in the underlying hosting environment.
What to do if your WordPress site is hacked
Malicious actors can harm your site in many ways, meaning there isn't a catch-all solution for every hacked-website situation. Some security breaches are more serious than others. Still, you can take general steps depending on the attack's severity.
If you suspect your site has been compromised, contact your hosting provider as soon as possible. They may be able to help contain the attack, preserve evidence, identify malicious changes, or restore a known-clean backup. Avoid making unnecessary changes until you understand the situation, especially if customer data may have been exposed.
What to do if you can still log into WordPress
If you've been hacked, but can still log into your WordPress site, the steps below can help mitigate further harm and restore your site:
Contact your hosting support. Explain what happened and ask them to help contain the compromise, check for server-level malware, and identify a safe recovery option.
Secure your accounts. Change potentially compromised passwords, including WordPress administrator, hosting, FTP/SFTP, database, and associated email credentials. Enable 2FA wherever available.
Check for suspicious users. Go to Users → All Users and review administrator accounts. If you find an account you don't recognize, report it to your host or security specialist and remove unauthorized access as part of the recovery process.
Run a malware scan. Use a reputable security tool such as Wordfence, Sucuri, or MalCare. Remember that detecting malware and removing it are different tasks.
Review recent posts and pages. Look for hidden spam, malicious redirects, or content you didn't publish. If you aren't comfortable examining code, ask your hosting provider or a WordPress security specialist for help.
Check WordPress files and configuration. Files such as .htaccess and wp-config.php may contain unauthorized changes. Because these files can contain sensitive settings and credentials, don't paste their contents into public AI tools. If you're unsure what to look for, have your host or a qualified professional inspect them.
Update vulnerable software. Once you've contained the compromise and your recovery plan is clear, update WordPress core, themes, and plugins. Remove unused or abandoned software.
Restore from a known-clean backup if appropriate. Make sure the backup predates the compromise, and address the vulnerability that allowed the attack so the restored site doesn't get infected again.
Continue monitoring. Check for suspicious login attempts, unauthorized changes, and signs that the attacker still has access.
What to do if you can't log into WordPress
If attackers have taken complete control of your site and locked you out, the solution becomes more technical. The first step isn't, though: Immediately contact your hosting support, explain you've been locked out due to a suspected hack, and ask if they can help secure the account, restore access, scan for server-level malware, or recover from a clean backup.
If they can't help right away, avoid making direct database changes unless you have the necessary technical experience and a reliable backup. Tools such as phpMyAdmin or your hosting provider's database manager can access WordPress user records, but deleting or changing the wrong entries can cause further problems. A qualified WordPress security professional can help investigate suspicious administrator accounts and restore access safely.
5.0
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Web hosting service rated best overall in our hands-on testing of 20+ providers
Hit 100% uptime and a 99/100 page speed score across all three test locations
Includes an AI content creator, image generator, and WordPress troubleshooter alongside the web builder
Bottom line: Is WordPress security difficult to maintain?
Not necessarily, but protecting your WordPress site against hackers isn't a 100% set-it-and-forget-it solution. You can handle some steps during initial setup, like choosing the right host, installing a security plugin, and setting up 2FA, but truly hardening your WordPress site takes ongoing effort.
You need to stay on top of WordPress updates, plus any themes or plugins you have installed, and if you run a multi-user site, assign proper user roles to new registrants. Both require periodic audits and cleanups if you find any themes, plugins, or users that are no longer active.
Use strong, unique passwords, and change them if you suspect they've been compromised. And don't forget backups. Some hosts include them automatically, but if they don't, you'll need to set a schedule to do them manually.
To put this information to use, I recommend handling the one-time items first, then setting periodic reminders for the rest. The small time investment you make in WordPress security now will pay off silently for the life of your website.
FAQs
Is WordPress secure?
WordPress can be run securely, but it exists in a paradox: Because it powers 40.1% of all websites on the web,it has a massive target on its back, but at the same time, because of that popularity, it also has many developers constantly working on it to reduce the risk of attack. They do a lot, but site owners still need to secure their own sites. At a baseline, that means using a reputable WordPress web host, configuring logins and site access, updating WordPress to the latest version, and doing the same for themes and plugins.
How do I secure my WordPress site?
Securing a WordPress site requires a multi-front strategy that starts with choosing a reputable web host, preferably one that includes strong security features like an SSL certificate, a web application firewall (WAF), malware scanning and removal, uptime monitoring, and automatic backups. Keeping WordPress core files, themes, and plugins up to date matters, too. Finally, installing a WordPress security plugin, enabling 2FA, and limiting unsuccessful password attempts are also important.
Do I need a WordPress security plugin?
It's good practice to consider a reputable WordPress security plugin because it can help protect against brute-force attacks and detect suspicious activity. Depending on the plugin, it may also block malicious traffic, scan for malware, or offer 2FA login. Details vary by plugin, but no matter which one you install, it won't cover every aspect of WordPress security. WordPress sites also need secure hosting, proper access controls, frequent backups, and regular updates to themes, plugins, and WordPress core files.
What is the most important thing to do for WordPress security?
The single most important thing you can do to keep your WordPress site secure is to ensure you are always using the latest secure version of WordPress, as well as updated versions of any themes and plugins you've installed. The developers behind WordPress (and WordPress-adjacent companies like Patchstack) work day in and day out to neutralize emerging threats. Then they incorporate the fixes into updates. Reading an up-to-date WordPress security guide (like this one) will help you with additional best practices.
4.9
AllAboutCookies writers and editors score products based on a number of objective features as well as our expert editorial assessment. Our partners do not influence how we rate products.
Martin Dubovic reviews web hosting and AI app-building tools based on direct, hands-on experience. He builds and deploys websites professionally and brings more than 10 years of developer experience to his recommendations. He has authored more than 55 All About Cookies articles focused on AI app builders, web hosting, website builders, and domains, and he also runs Bizzaro Devs, a developer-focused tech newsletter.